
A practical accountability framework for CIOs, operations leaders, and integration teams
A customer is marked “won” in the CRM. An integration creates the billing account. Another workflow provisions access in a service platform. Three applications report success individually, yet the customer still cannot use the service. Sales says the deal is closed. Finance sees an account. Support sees no active entitlement. Who owns the failure?
This is not primarily a connector problem. It is an ownership problem. An integration ownership model defines who is accountable for the complete business outcome, who operates the technology, who controls each source of truth, and who resolves exceptions when the workflow crosses organizational boundaries.
The distinction matters because an API call can return HTTP 200 while the business process remains incomplete. A workflow is only successful when the agreed business state exists across the required systems, within the agreed time, with a traceable record of what happened.
The short answer: one business owner, one operational lead, clear system custodians
For each business-critical cross-system workflow, appoint a named business process owner accountable for the end-to-end result and a named technical integration owner responsible for reliable execution. Each application retains its own system owner, while data stewards and security teams own the decisions within their mandates. A vendor or implementation partner may deliver components or support incidents, but does not automatically inherit the company’s accountability for customer outcomes.
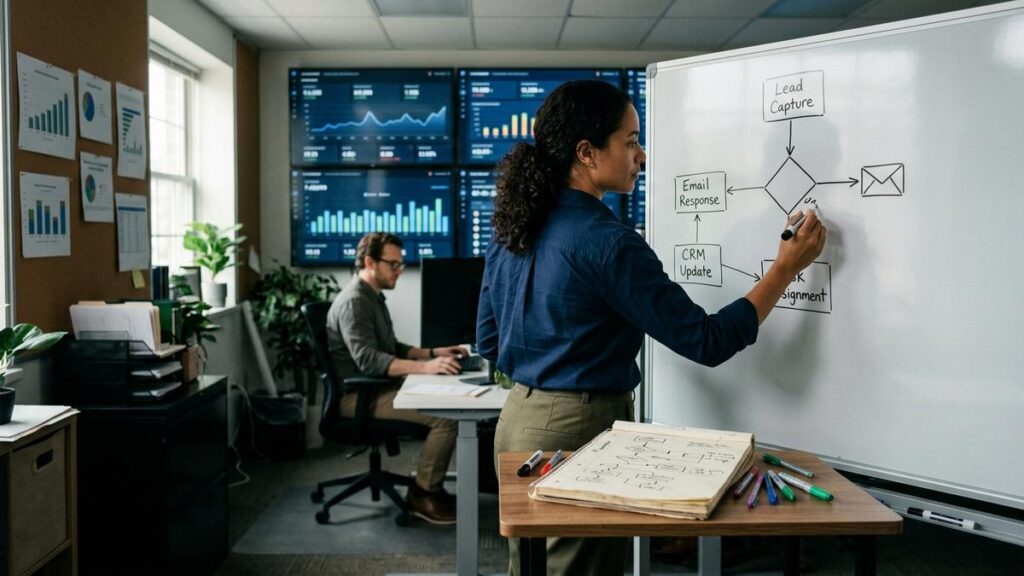
Avoid assigning “IT” or “Operations” as the only owner. A department name is not an escalation contact, and a technical administrator should not decide whether a disputed customer is eligible for service. Conversely, a business owner should not be expected to debug token refresh failures or queue backlogs.
This article explains the roles, decision rights, records, incident procedures, and management measures needed to make that division work in practice.
Why three connected applications create an ownership gap
Imagine a subscription onboarding workflow: the CRM owns sales opportunities, the billing platform owns invoices and payment status, and the service platform owns provisioning. A middleware service, iPaaS workflow, or custom integration coordinates them. Each application has an administrator and a vendor support team. Yet no single application owns “customer successfully onboarded.”
The failure modes are familiar. A CRM field is renamed without notifying downstream teams. A billing status maps incorrectly to a service entitlement. An employee who created the OAuth connection leaves the company. A retry creates a duplicate account. A webhook arrives late, and a support representative manually fixes the wrong record. Each team can truthfully report that its own system is healthy.
The underlying issue is fragmented accountability. Application ownership, integration ownership, data ownership, and business process ownership are related but not interchangeable. A useful operating model separates them explicitly and reconnects them through a shared workflow definition.
Five ownership roles that should not be collapsed
1. Business process owner: accountable for the outcome
Typically a director of revenue operations, finance operations, customer success, or another process leader. This person defines what “complete” means, acceptable delays, customer impact, exceptions requiring human approval, and the priority of changes. They accept or reject the business result after major releases. They also authorize trade-offs when a workaround creates financial, compliance, or customer consequences.
For the onboarding example, the business owner might define success as: a valid CRM contract, a billing account with the correct plan, and an active service entitlement within a specified window. The target is a business policy to agree, not a generic technical SLA.
2. Technical integration owner: responsible for execution
Usually an integration engineer, platform lead, or application engineering team. This owner maintains orchestration logic, mappings, retries, observability, deployment, runbooks, and technical escalation. They ensure a failed or ambiguous transaction is detected and routed, rather than silently abandoned.
If an integration is outsourced, the internal technical owner still needs access to architecture, logs, deployment procedures, source code or platform configuration as contractually appropriate, and a documented vendor escalation path. “The vendor handles it” is not an operational model unless response obligations, evidence, access, and continuity are defined.
3. Source-system owners: accountable for local configuration and interfaces
The CRM administrator owns the CRM configuration and its change process; the billing administrator owns billing settings; the service-platform owner owns provisioning configuration. They review upstream and downstream impact before changing fields, statuses, permissions, API versions, or automation rules.
A source-system owner can approve a local change but should not unilaterally approve a change that alters the meaning of an end-to-end business process. Cross-system effects require coordination with the process and integration owners.
4. Data and control owners: accountable for meaning and protection
A data steward defines authoritative identifiers, field semantics, allowed transformations, and quality rules. Security or identity teams approve access patterns, service identities, secret storage, and privileged scopes. Finance or compliance may need decision rights over tax, payment, retention, or audit requirements.
These roles do not have to attend every incident. They need explicit involvement triggers: a new sensitive field, an expanded OAuth scope, a changed financial calculation, a new retention rule, or an unresolved conflict over the system of record.
5. Incident commander or service desk: responsible for coordinated response
During a material outage, a designated incident lead coordinates triage, communication, and recovery. That person may differ from the integration owner. A cross-functional incident should have one coordination channel and one incident record, not three disconnected vendor tickets.
The incident lead does not invent business policy. If a partial refund, service suspension, or manual entitlement override is required, the authorized business owner makes that decision and the incident record captures it.
Use a small RACI, but attach real decision rights
A RACI matrix distinguishes Responsible (does the work), Accountable (owns the outcome), Consulted (provides input), and Informed (receives updates). It is useful only when the names, authority, and escalation route are current. Microsoft’s governance guidance recommends using RACI to clarify cross-team responsibilities; the point is decision clarity, not filling a spreadsheet with initials.
An illustrative assignment for CRM-to-billing-to-service onboarding might be:
- Define completion criteria and customer-impact thresholds: business process owner A; operations analyst R; integration lead C.
- Maintain mappings, orchestration, retries, and monitoring: integration lead A/R; application owners C.
- Approve CRM field or status changes: CRM owner A/R; integration lead and business owner C when downstream behavior changes.
- Approve entitlement or billing-policy exceptions: business process owner A; relevant operations team R; finance/security C as needed.
- Rotate or replace integration credentials: identity/platform owner A; technical integration owner R; SaaS administrator C.
- Resolve a cross-system production incident: service/incident lead A for coordination; integration lead and affected system owners R; business owner A for business-impact decisions.
- Accept a workflow release: business process owner A for business acceptance; integration lead R for technical readiness; system owners C.
Notice that accountability is defined per decision, not as one universal person for every action. One named business owner remains accountable for the overall process, while specialized owners retain authority over security, financial controls, and platform operations. If your matrix shows three “A” entries for the same decision, rewrite the decision boundary.
Create an integration register that connects business and technical views
An integration inventory should be usable by an operations leader during an incident, not only by an architect during design. Start with the workflow as the top-level object, then list the interfaces that implement it. A single workflow may have multiple API calls, queues, scheduled jobs, and manual checkpoints.
For each critical workflow, record the following:
- Business purpose, process owner, technical owner, and backup contacts.
- Trigger and expected final business state, including the authoritative system for each key field.
- Source and destination applications, environments, integration platform, and interface identifiers.
- Data contract, key mappings, transformation rules, and handling of null, unknown, and deleted values.
- Expected volume, maximum acceptable lag, operating hours, and recovery priority.
- Authentication method, credential custodian, scopes, rotation procedure, and expiry alerts.
- Monitoring links, correlation IDs, processing ledger, alert routing, and runbook.
- Exception classes, manual approval rules, reconciliation method, and replay safeguards.
- Vendor contacts, maintenance windows, API version dependencies, and change-notice subscriptions.
- Last tested recovery, last ownership review, and next planned control review.
Keep this register in a controlled location that owners can update. Link to source-controlled configuration and operational dashboards rather than duplicating every technical detail. Review it whenever an application is replaced, a vendor changes its API, or a business process is redesigned.
Decide the system of record field by field
“CRM is the master” is usually too broad. The CRM may be authoritative for opportunity stage, the billing system for paid-through date, and the service platform for actual activation time. A customer email address might be editable in more than one system, but that does not mean every update should overwrite every other copy.
Create a field-level ownership map for high-impact entities: customer, contract, subscription, invoice, entitlement, employee, and product. For each field, specify who can originate a change, which system publishes it, which systems consume it, how conflicts are resolved, and whether history must be retained.
Where two systems legitimately accept edits, define conflict precedence and timing. A simple “last write wins” rule can silently reverse a verified correction if an older event arrives late. Prefer explicit source priority, version checks, and exception review for sensitive records.
The same principle applies to identifiers. Store the mapping between CRM customer ID, billing customer ID, and service account ID. Use stable identifiers rather than matching on mutable names or email addresses. Define what happens when records merge, split, or are deleted.
Who owns mappings and exceptions when business rules change?
A mapping table is not merely code. Translating “Trial,” “Active,” “Suspended,” and “Cancelled” between platforms may encode eligibility, revenue recognition, and customer experience. The business owner approves the intended meaning; the technical owner implements and tests it; source-system owners confirm their local status definitions.
Maintain a versioned mapping specification with sample input, expected output, unknown-value behavior, and approval history. Do not silently default an unfamiliar status to “Active.” For high-impact unknown values, quarantine the record, raise a classified exception, and preserve the source payload or a privacy-safe reference.
Separate transient technical exceptions from business exceptions. A timeout or rate-limit response may be retried under a bounded policy. A missing tax identifier, ambiguous customer match, or conflicting plan entitlement usually needs correction or approval. Repeated retries cannot resolve missing business information.
For practical details on idempotency, backoff, webhooks, and replay, see Actiknow’s API retry and webhook design guidance. Those technical controls support the ownership model; they do not replace decisions about who may authorize a business override.
Credential ownership should survive employee turnover
One of the most avoidable integration failures occurs when a production connection depends on a personal account, an undocumented OAuth consent, or a secret known only to a contractor. The workflow may operate for months until an employee leaves, a password changes, or an access policy is tightened.
Inventory each integration identity, the provider tenant it belongs to, the permissions granted, where its credentials are stored, its expiry or rotation method, and the responsible custodian. Prefer supported service identities, managed identities, or workload federation when available. Some SaaS providers require user-authorized connections; document that constraint and create a tested reauthorization process.
The identity or security owner approves the access model. The technical integration owner implements rotation and monitoring. The business process owner understands the business consequence of a lost connection. Never store tokens in the workflow register or incident tickets.
Change control must follow the dependency chain
A SaaS release can change an API, a field type, a permission scope, or the meaning of a status without changing the integration’s own source code. The integration owner therefore needs a vendor-change watchlist and an impact map, not just an internal deployment calendar.
For material changes, require a short cross-system change record: proposed change, initiating owner, affected interfaces, data and business rules, test evidence, rollback or containment option, release window, and business acceptance. Contract tests should validate consumer assumptions; end-to-end tests should validate the final business state.
Differentiate routine configuration updates from changes that alter financial calculations, eligibility, authorization, or customer communications. The latter need business sign-off even if they involve only one line of mapping code.
When the application landscape becomes complex, architectural decisions about direct APIs, iPaaS, or a reusable integration layer also influence who can operate and change the workflow. Actiknow’s guide to SaaS integration architecture choices explains the trade-offs. Ownership should be explicit whichever architecture is selected.
A realistic failure: the payment succeeded, but access was never granted
Consider this hypothetical example. A customer pays an invoice. Billing emits an event that should activate the subscription in the service platform. The webhook is received and acknowledged, but the downstream provisioning call fails because the service platform rejects an obsolete plan code.
A weak operating model stops at “billing is fine” and “the integration returned an error.” A strong model produces a different sequence:
- The integration records the business transaction ID and correlation ID, including the source event, target call, and current processing state.
- An alert identifies a provisioning exception that has exceeded the agreed customer-impact threshold, not merely an elevated HTTP error count.
- The technical owner confirms that replay is safe and that the failure is a non-transient mapping error.
- The business owner or authorized operations delegate decides whether temporary access is permissible while the plan mapping is corrected.
- The source-system owner confirms the current valid plan codes; the integration owner changes and tests the mapping.
- The failed event is replayed once under an idempotent process, and the resulting entitlement is verified in the service platform.
- The incident is closed only after reconciliation confirms the invoice, customer, and entitlement agree, and affected stakeholders receive an update.
This is a hypothetical workflow illustration, not an Actiknow client case study. Its value is showing how technical restoration and business restoration differ. Reopening the webhook endpoint is not the same as activating the customer.
Build a reconciliation control, not just a monitoring dashboard
Monitoring answers “is the integration running?” Reconciliation answers “did the intended business outcome occur?” Both are necessary. An API success rate can be excellent while records are missing, duplicated, mapped incorrectly, or stale.
Choose a comparison that reflects the business process. For onboarding, compare eligible CRM contracts with billing accounts and active service entitlements. Match on governed identifiers, account for legitimate processing delays, and classify differences by cause. For a finance workflow, reconcile approved invoices to posted transactions and investigate unmatched or duplicate entries.
A practical reconciliation report includes source count, eligible count, completed count, pending within SLA, overdue, rejected by business rule, duplicates, and unresolved mismatches. Show the oldest unresolved item and its owner. Use thresholds based on business exposure, not arbitrary percentages.
Reconciliation should be actionable. Every unresolved difference needs a case ID, assigned resolver, next action, escalation deadline, and closure evidence. For irreversible actions such as payment or refund, confirm remote state before replaying an uncertain write.
Define incident ownership before the first outage
A runbook should say who receives alerts, who acknowledges them, where to find logs, how to determine business impact, what can be retried automatically, what requires approval, and how to validate recovery. AWS operational guidance emphasizes runbooks with clear owners, error handling, permissions, and escalation paths.
Set severity by consequence. An internal report arriving late may be lower priority than a customer being charged twice or access being provisioned incorrectly. Define who can authorize a temporary manual workaround and how the workaround is reversed or reconciled afterward.
Use a single incident timeline across vendors and teams. Record the earliest known failure, affected transactions, decisions, communications, mitigation, reconciliation results, and follow-up controls. Do not close the incident simply because the queue is empty if the business process still contains exceptions.
A 30-day implementation plan for CIOs and operations leaders
Week 1: identify critical workflows and owners
Select five to ten workflows based on customer impact, financial exposure, operational dependency, and change frequency. Draw a simple journey from trigger to final state. Name the business owner, technical owner, system custodians, and backups. Identify any workflow with no single end-to-end accountable person.
Week 2: map decisions and controls
Document systems of record, critical fields, mappings, credentials, and known exception classes. Build a compact RACI for business acceptance, security approvals, release decisions, and incident response. Agree on a few measurable completion criteria and recovery expectations.
Week 3: instrument and test
Add correlation identifiers, status tracking, and exception routing where missing. Create a basic reconciliation query or report for each pilot workflow. Test an expired credential, an unknown status, a duplicate event, and a downstream outage in a safe environment. Ask a backup owner to execute the runbook.
Week 4: run an operational review and expand
Review actual exceptions, alert ownership, time to restore business state, and any missing approvals. Fix the highest-risk gap first. Establish a monthly owner review and quarterly dependency review. Expand the pattern to additional workflows only after the first set can be operated reliably.
The executive scorecard: measures that reveal ownership quality
Measure the operating model, not only connector uptime. A concise scorecard can include:
- Critical workflows with a named business owner and technical owner, as a percentage of the inventory.
- Workflows with tested reconciliation and an agreed business completion criterion.
- Overdue business exceptions, by age, financial exposure, and accountable team.
- Median and high-percentile time from source event to verified downstream completion.
- Incidents detected internally before users report them, with clear definitions.
- Critical credentials with a named custodian and tested renewal or reauthorization procedure.
- Changes released with cross-system impact assessment and business acceptance where required.
- Recovery exercises completed, including evidence that business records were reconciled afterward.
These are suggested measures, not industry benchmarks. Set baselines from your own workflows and make the definitions auditable. A 100% green technical dashboard is not useful if customers still have unresolved exceptions.
Common mistakes to avoid
- Naming the integration vendor as the sole owner and leaving internal decision rights undefined.
- Making IT accountable for business rules it has no authority to approve.
- Assuming the source application owner also owns every downstream consequence.
- Documenting connectors but not the end-to-end workflow or final business state.
- Treating HTTP success, queue completion, or dashboard freshness as proof of reconciliation.
- Sharing personal credentials or leaving OAuth consent tied to departing employees.
- Retrying business-rule failures automatically without limits or authorization.
- Creating a RACI that is never exercised during change reviews or incidents.
- Requiring so many approvals that urgent recovery becomes impossible.
The objective is proportionate control. A low-risk notification workflow may need a simple owner and retry policy. A payment, identity, payroll, or customer-entitlement workflow warrants stronger evidence, decision rights, and recovery testing.
Frequently asked questions
Who should own an integration between CRM, ERP, and a third SaaS system?
The business process owner should be accountable for the complete business outcome, while a technical integration owner operates the cross-system flow. CRM, ERP, and other application owners retain responsibility for their respective interfaces and configurations.
Is the business owner also responsible for fixing API failures?
No. The business owner defines outcomes, priorities, and acceptable exceptions. Engineers or platform operators diagnose and repair technical failures. The business owner approves decisions that change customer, financial, or operational outcomes.
What is the difference between an application owner and an integration owner?
An application owner manages a specific system’s configuration, availability, and change controls. An integration owner manages how data and actions move between systems, including orchestration, monitoring, mappings, and technical recovery.
Does an iPaaS platform eliminate the need for an ownership model?
No. An iPaaS can centralize connectors, credentials, and workflow execution, but it cannot determine the company’s business policies or approve disputed transactions. Platform convenience does not transfer accountability.
Who approves data mapping changes?
The relevant business or data owner approves semantic changes. The technical owner implements and tests them. Source-system owners confirm local field definitions, and control owners review changes involving sensitive data or financial rules.
Who should own API credentials?
A named identity, security, or platform custodian should govern access, with the integration owner responsible for technical implementation and renewal. Critical connections should not depend invisibly on a personal account.
How do we handle a vendor API change?
Track vendor notices, identify dependent workflows, assess the business impact, update contracts and mappings, test in a controlled environment, and secure the appropriate approvals before release. Maintain a containment or rollback option where feasible.
What if a transaction succeeded in one system but failed in another?
Preserve its correlation ID and processing history, classify the failure, avoid unsafe duplicate writes, and reconcile the final business state. A designated resolver handles the exception, with business approval for material manual overrides.
How much documentation is enough for a small organization?
Start with a one-page workflow record, named owners, a field-level source-of-truth map for critical data, an exception route, and a tested runbook. Expand documentation in proportion to risk and complexity.
How often should integration ownership be reviewed?
Review owners when people, vendors, systems, or workflows change. For critical workflows, a regular operational review and a periodic dependency and access review are sensible starting points. Choose the cadence based on change frequency and risk.
Conclusion: ownership is an operating capability, not a box on an architecture diagram
The most useful integration ownership model answers four questions without a meeting: what business outcome should exist, who can decide when it is wrong, who can restore the technical flow, and what evidence proves the process is complete. Assign those answers before the next outage or vendor change.
Actiknow’s custom solutions and system integration services cover API-based connections, business applications, and automation. If your team is struggling with unclear ownership, fragile handoffs, or recurring cross-system exceptions, discuss your integration operating model with Actiknow. A focused review of one critical workflow is often a practical place to begin.
Selected reference guidance
Microsoft: Build a cloud governance team (RACI and decision rights).
AWS Well-Architected: Use runbooks to perform procedures (ownership, error handling, and escalation).