
An executive dashboard can be accurate, fast and beautifully designed yet still be an enterprise risk if the wrong audience can open it, download its data or change the underlying content. As Tableau adoption expands across departments, permissions become part of the analytics architecture rather than an administrative task performed after publishing.
The scalable answer is not to create a unique rule for every workbook and every employee. It is to design a small number of business-aligned groups, place governed content in predictable projects, enforce project-level rules where appropriate, and test what real users can actually do. This guide explains the architecture, the exceptions and the operating practices that make those choices reliable.
The executive decision: what should a permission model accomplish?
A sound Tableau authorization model should answer four questions without requiring a specialist to inspect dozens of workbooks: Who can discover and view this information? Who can publish or change it? Who can download or reuse underlying data? Who can approve and administer changes? If those answers vary unexpectedly between dashboards that serve the same audience, the organization has an access-design problem.
The goal is predictable access, not simply fewer permissions. A finance analyst may need to edit a planning workbook but only view a board dashboard. A regional manager may need access to the same dashboard as peers while seeing a different subset of rows. A platform administrator may need to administer content without becoming the business owner of every metric. These are distinct requirements and should be modeled separately.
A useful design principle is to separate identity, content organization, capabilities and data security. Tableau site roles establish the ceiling on what a user may do. Groups express the audiences to which a rule applies. Projects define the content boundary. Permission capabilities control actions on assets. Row-level and database controls determine which underlying records may be exposed. Treating any one of these as a substitute for the others produces gaps.
Understand Tableau’s four permission layers
1. Site roles define the maximum capability
Tableau Cloud and Tableau Server assign site roles such as Viewer, Explorer, Explorer (can publish), Creator and administrator roles. A Viewer cannot become a workbook editor merely because a group rule says Web Edit is allowed. Conversely, a Creator role does not automatically grant access to every workbook. The effective result depends on both the site role and the content rules. Tableau documents this distinction in its site roles and licenses reference.
Plan licenses and site roles from actual responsibilities. Viewers should consume approved reports. Analysts who need browser-based exploration may need Explorer capabilities. People creating and publishing data sources or advanced content may require Creator. Use administrators for platform administration, not as a shortcut for difficult project permissions. Review these assignments when job responsibilities change.
2. Groups express business audiences
Create groups that correspond to durable access needs: for example, Finance-Consumers, Finance-Publishers, Sales-Regional-Managers and BI-Platform-Admins. These are illustrative naming patterns, not prescribed Tableau defaults. Prefer group rules to individual user rules because employee onboarding and departures then become membership changes rather than edits to every affected asset.
Avoid groups that mix unrelated privileges, such as Everyone-Who-Needs-Anything. Equally, avoid a group for each workbook unless the access boundary genuinely differs. Keep a short description of every group, its business owner, the membership source and the expected capabilities. Where identity-provider synchronization is available, coordinate group lifecycle with IT and verify that changes propagate as intended.
3. Projects organize governed content
Projects are the main unit of scalable Tableau content governance. A project can represent a domain, an audience, a lifecycle stage or a combination. Examples include Finance / Certified Production, Sales / Published Analytics and Shared / Approved Data Sources. The naming scheme matters less than consistency and clear ownership. Avoid deep hierarchies that make it hard to identify which project controls permissions.
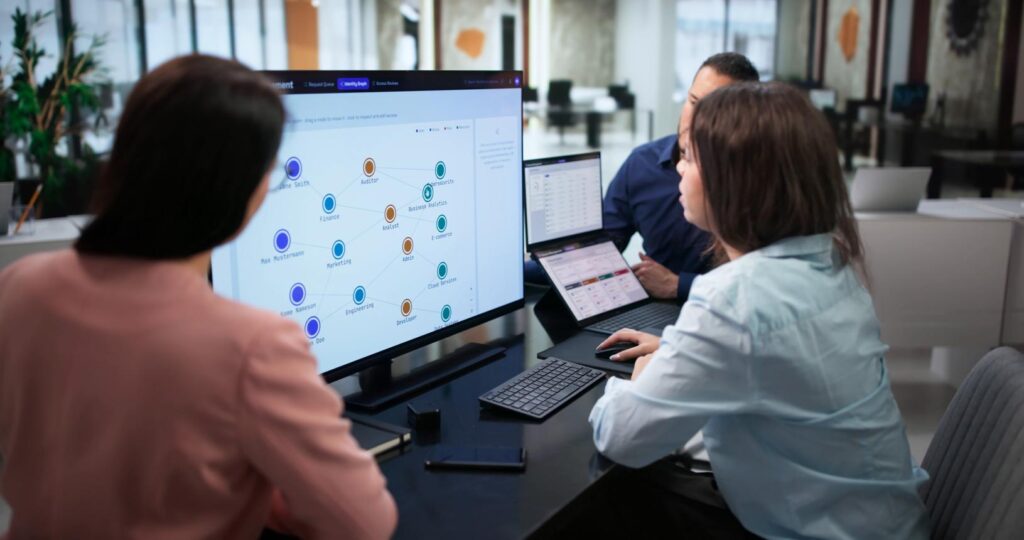
At the project level, configure the relevant content-type tabs, including workbooks and data sources. Granting View on a project container is not the same as granting every capability on the workbooks it contains. Tableau’s permissions guidance recommends setting rules at the project level and for groups, rather than maintaining workbook-by-workbook user exceptions.
4. Content permissions define specific actions
Permission capabilities cover actions such as View, Web Edit, Download Summary Data, Download Full Data, Download Workbook, Connect, Overwrite and Set Permissions, depending on the asset type and the user’s site role. Do not assume that allowing someone to view a dashboard also entitles them to extract its data or republish a copy. Treat download and publishing capabilities as explicit business decisions.
This distinction is especially important when sensitive aggregates appear harmless but underlying records contain customer, employee or commercially sensitive information. For every audience, specify what users may view, export, modify and redistribute. A small, documented capability matrix is easier to maintain than informal assumptions about what a Viewer or Explorer can do.
Design a project structure that survives growth
Start with an inventory, not a reorganization. Identify the current projects, workbooks, published data sources, flows, owners, audience groups and existing exceptions. Note whether each project is locked or customizable, which dashboards are business-critical and where content is shared across departments. Without this baseline, a tidy new hierarchy can accidentally break access or preserve the wrong permissions.
One practical enterprise pattern is to separate development and production publishing. Development projects can be customizable for controlled authoring. Certified or executive production projects should usually be locked so content owners cannot silently grant wider access to an individual workbook. Separate sensitive domains such as payroll, finance and customer-level operations when their access requirements differ.
Do not create a new Tableau site for every department by default. Sites are broader administrative boundaries with their own users, content and governance implications. A single site with well-designed projects may be easier to operate when audiences share common identity and reporting assets. Multiple sites can be justified by strong isolation, administrative or organizational requirements, but introduce their own management overhead.
Locked versus customizable projects
In a locked project, project-level rules are enforced on the content governed by that lock. In a customizable project, project rules act as defaults but authorized owners and administrators can change permissions on individual assets. This flexibility is valuable in collaborative development but is usually undesirable for standardized executive reporting. Tableau recommends locking projects when predictable content access matters.
There is a material difference between locking a project alone and locking it including nested projects. A parent lock that includes children enforces the parent’s rules throughout that hierarchy. A lock that excludes nested projects lets children have independent settings. Before changing this setting, inspect the existing child permissions because switching to a lock can overwrite content-specific rules. Document the intended blast radius and test in a controlled area.
Content moves also deserve explicit review. Moving an asset into a locked project enforces the destination’s permission model, while moving it into a customizable project can preserve existing asset rules. A migration therefore needs a before-and-after entitlement check, not merely confirmation that the workbook appears in the new folder. Tableau’s project permission management documentation explains these behaviors.
Treat the Default project as a template, not a dumping ground
New top-level projects inherit initial permission rules from the Default project, although they do not inherit its asset-lock setting. Audit Default before scaling your hierarchy. If Default grants broad publishing or viewing capabilities, new projects may begin with permissions that are wider than intended. Keep it intentionally configured, with clear ownership and a documented process for creating production projects.
Also review the All Users group. Tableau recommends removing its rule or setting capabilities to None where you want explicit group-based access. Do not confuse None or Unspecified with an explicit Denied rule: an explicit group denial can override an allowance from another group. Because everyone belongs to All Users, an indiscriminate Denied rule can create widespread access failures.
How Tableau calculates effective permissions
A user can belong to multiple groups, have an individual rule, own a workbook and hold a site role that limits certain actions. Tableau evaluates these factors in a defined order. Administrators, project owners and project leaders have special capabilities; individual rules are evaluated before group rules; and conflicting group rules can deny a capability. The practical lesson is to inspect effective permissions, not infer them from a single group row.
Consider an illustrative scenario. Priya belongs to Finance-Consumers and a temporary Restricted-Exports group. The first group allows workbook viewing and summary downloads. The second denies downloading summary data. Priya may still be able to view the dashboard but cannot download summary data if the group denial governs that capability. An individual allowance can have different precedence. The exact outcome should be checked in the effective-permissions grid.
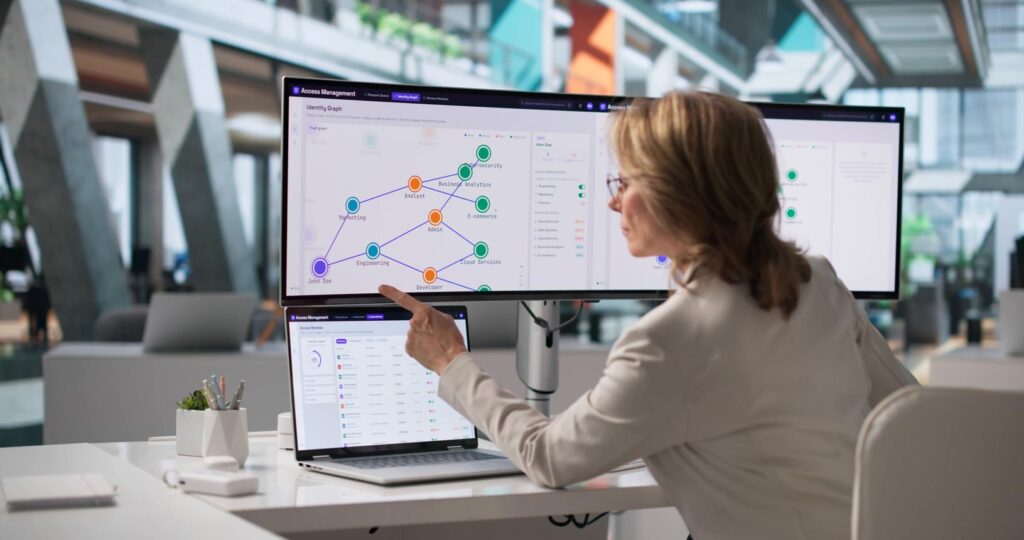
Unspecified does not mean a universal grant or a permanent block. It means the rule does not decide that capability, allowing other applicable rules to be evaluated. If no rule grants the capability, the effective result is denied. Use Tableau’s effective permissions reference when designing exceptions, and validate a named test account for each audience rather than relying on mental arithmetic.
Owners and project leaders are particularly important exceptions. Project leaders can administer content throughout their applicable project hierarchy, subject to site-role limits. Content owners also have broad rights, although a locked project restricts their ability to change permissions. Keep the list of project leaders short, review it periodically and do not use project leadership as a routine publishing role.
A practical access matrix for enterprise Tableau
Use a capability matrix as a design artifact. For example: Executive Consumers may View approved production workbooks but may not Web Edit or download underlying full data. Department Analysts may View and interact with production content, while publishing only to their departmental development area. Certified Publishers may publish approved workbooks and data sources to designated projects. Project Leaders may manage the relevant project’s content and access rules. Site Administrators manage the site, with assignment tightly controlled.
The matrix must be implemented separately for relevant asset types. Workbook View is not a replacement for published data-source Connect; project Publish is not a substitute for workbook Overwrite. Determine whether a workbook uses embedded credentials, published data sources or live connections, and test the entire access path. For sensitive workflows, include subscriptions, extracts, exports, embedded experiences and any external integrations in the review.
For each matrix row, capture the group, site-role requirement, permitted actions, explicitly prohibited actions, business approver, technical owner and review frequency. This is a governance document, not an excuse to grant every possible capability. Start with minimum access, then add a capability only when a tested workflow requires it.
Do not confuse Tableau content access with row-level security
Project and workbook permissions determine who can open or act on a Tableau asset. They do not, by themselves, guarantee that two authorized users see different customer or regional records. If users should see different rows within the same dashboard, implement and test row-level security using an appropriate Tableau or data-platform approach. Apply database permissions and credential management consistently with that design.
For example, a regional sales dashboard may be viewable by all regional managers, but each manager should see only authorized territories. A user filter or entitlement table may be appropriate, depending on the architecture and threat model. Verify the behavior in the published environment, including extracts, live connections and exports. Do not treat a hidden sheet, filtered dashboard view or navigation trick as a security boundary.
Published data sources can improve reuse, but they also create a second authorization surface. A user who cannot open a workbook may still have permissions to connect to a published data source, or vice versa. Review data-source permissions separately, and test whether users can create a new workbook, download a data source or access fields that the original dashboard did not display.
Publishing, embedding and external consumption
A dashboard embedded in a portal does not automatically inherit the portal’s business permissions. Authentication, Tableau identity, connected-app settings and Tableau content entitlements must work together. For embedded analytics, test direct Tableau URLs, copied links, session expiry and changes in user group membership. A secure-looking portal is not evidence that its underlying Tableau content is protected.
The same principle applies when analytics is consumed through APIs or AI-assisted workflows. If a service identity has broad access, downstream applications may expose information beyond an individual user’s entitlement. Define whether each request is executed under delegated user identity or a tightly scoped service account, and validate both the query surface and the response. Actiknow’s related discussion of governed analytics and agent access explores these risks in another Tableau integration context.
How to audit permissions without creating another spreadsheet problem
An access audit should answer who has effective access to high-risk content, why that access exists and when it was last approved. Build a repeatable inventory of users, site roles, group memberships, projects, content owners, permission rules and exceptions. Flag assets with individual-user rules, production projects that remain customizable, broad download privileges, orphaned owners and stale groups.
Tableau Cloud offers Admin Insights data sources for governance analysis, including Groups, Site Content and Permissions. The Permissions data source can help identify explicit rules and their context, but administrators should still interpret effective permissions carefully because site roles, ownership and inherited locks affect the final result. In Tableau Server environments, use supported administrative views, APIs or appropriate repository-based analysis under controlled access.
A useful governance dashboard can track the number of individual exceptions, percentage of production projects locked, percentage of assets with named business owners, number of privileged project leaders, unreviewed group memberships and failed access tests. These are control-health indicators, not proof of security by themselves. The meaningful outcome is whether access decisions are explainable and reproducible.
A safe migration from ad hoc rules to governed projects
Phase 1: Discover and classify
Inventory the site and identify the first high-value domain to govern. Classify each workbook as certified production, departmental collaboration, development or archive. Record its owner, users, data sensitivity, published data sources and any current exceptions. Ask business owners which actions are genuinely needed. Do not infer requirements solely from current permissions, because current rules may be historical accidents.
Phase 2: Define groups and project boundaries
Agree on the group naming convention, identity-management owner and approval process. Create a target project tree with explicit owners and documented lock settings. Draft the capability matrix for projects, workbooks, data sources and other relevant asset types. Set up representative test accounts: an executive consumer, an analyst, a publisher, a restricted user and an administrator.
Phase 3: Pilot in a controlled domain
Choose a domain with manageable complexity but real business usage. Recreate or move a limited set of workbooks and data sources, apply group-level rules and lock the production project when ready. Test expected access and expected denial for each persona. Include attempts to download data, edit workbooks, publish content, connect to data sources and open a direct URL.
Phase 4: Reconcile and roll out
Compare the old and new entitlement lists. Resolve missing access with the business owner instead of silently adding individual exceptions. Communicate changes before moving high-visibility executive dashboards. Keep a rollback plan, the prior permissions export and an agreed support contact. Roll out by domain, review incidents and adjust the template before proceeding to the next group.
Testing scenarios that catch real-world mistakes
Positive tests confirm that the correct audience can perform an approved task. Negative tests confirm that an unauthorized audience cannot perform it. Both matter. Test a newly onboarded user, a user removed from a group, a person in two conflicting groups, a content owner, a project leader, and an employee whose site role does not permit the action requested by a rule.
Test direct workbook URLs as well as project navigation. Verify downloads separately from viewing. Test published data-source Connect and any permitted reuse. Test what happens when content moves between locked and customizable projects. Where row-level restrictions apply, compare actual visible records and exports for users from different regions or departments. Capture evidence of the results and the configuration version.
For sensitive projects, run a quarterly entitlement review and an additional review after major organizational changes. An access review should not simply ask managers to approve a long list of names. Provide the purpose of each group, the content it unlocks, the capabilities involved and the last observed usage where available. That context makes approvals more meaningful.
Common permission anti-patterns
Anti-pattern: granting access to named users on individual workbooks. This solves today’s ticket but creates tomorrow’s audit problem. Prefer group membership changes, with time-limited exceptions that have an owner and expiry date.
Anti-pattern: making every analyst a project leader. Project leaders can administer substantial content in their hierarchy. Separate publishing responsibilities from access administration, and give leadership only to the people who genuinely own that project.
Anti-pattern: placing all production dashboards in one broad project. A single locked project is predictable, but it is not useful if finance, HR and sales need materially different access. Split projects by meaningful governance boundaries, not by every visual or every report.
Anti-pattern: using explicit Denied everywhere. Denials are appropriate when intentional, but overlapping group membership makes them difficult to reason about. Use narrow positive grants and remove broad default rules where practical. Test the effective result.
Anti-pattern: treating dashboard filters as a security control. Filters improve usability; access boundaries require enforceable row-level, data-source and underlying platform controls. Validate access from alternative clients and download paths.
Anti-pattern: measuring success by the absence of complaints. Users may never notice that another department can view an inappropriate workbook. Audit both expected access and unexpected access, and monitor new publishing behavior after rollout.
A four-week implementation roadmap
Week 1
Inventory the current site, extract the group and permission structure, identify sensitive projects, and select the pilot domain. Deliverables: baseline entitlement inventory, risk register, asset ownership map and test personas.
Week 2
Design the target project tree, group structure, capability matrix and exception policy. Review with IT, security and business owners. Deliverables: approved permission design, identity-management responsibilities and a migration checklist.
Week 3
Configure the pilot, migrate a limited set of content and run positive and negative tests. Resolve issues with source-data access, download rights and ownership. Deliverables: evidence-backed test results, revised runbook and rollback instructions.
Week 4
Roll out the pilot pattern to additional approved projects, publish the access request process and establish a recurring review. Deliverables: production permissions baseline, ownership register, audit dashboard specification and operational handover.
What executives should ask before approving the architecture
Can we explain a user’s access to a sensitive dashboard in under five minutes? Is the production project locked, and does that lock cover its nested projects as intended? Who can grant access or change a workbook? Can users download more data than their role requires? Are published data sources and embedded views included? Does the team test both access and denial? Who reviews entitlements after staff or organizational changes?
If these questions have clear, testable answers, the model is likely ready to scale. If the answer depends on knowing which administrator last edited a workbook permission, the organization should simplify its design before expanding its Tableau footprint.
Frequently asked questions
1. What are Tableau permissions best practices for a large organization?
Use groups for audiences, project-level rules for content, locked production projects where appropriate, narrowly scoped site roles, explicit download decisions and regular effective-permission testing. Keep individual exceptions rare, approved and time-bound.
2. Are site roles the same as permissions?
No. Site roles set the maximum actions a user may perform; content permissions decide which of those actions are allowed on particular assets. A Creator role does not automatically grant access to every workbook, and a Viewer cannot become a publisher through a workbook rule.
3. Should every Tableau project be locked?
Not necessarily. Locked projects are a strong default for certified production content. Customizable projects can be appropriate for controlled collaboration and development. Choose deliberately, and document how nested projects inherit or manage their rules.
4. Why can a user be denied when their group is allowed?
Another group may explicitly deny the same capability, a user rule may take precedence, the site role may not permit the action, or a content-level rule may control the result. Inspect the effective-permissions grid rather than the single group rule.
5. What is the difference between None and Denied?
None or Unspecified means that rule does not grant the capability. Another applicable rule may still grant it. An explicit Denied is a negative rule that can override an allowance at the same evaluation level, so broad denials need careful testing.
6. Can Tableau groups be synchronized from an identity provider?
Group-management options depend on Tableau Cloud or Server, identity configuration and licensing. Where supported, identity-provider integration can reduce manual membership maintenance. Always verify synchronization, group naming, deprovisioning and effective access after changes.
7. Do locked projects prevent all changes to workbooks?
No. Locking standardizes permission rules; it is not a blanket prohibition on editing or publishing. Users with the required site role and allowed capabilities may still edit content. Administrators and project leaders retain special authority.
8. Does restricting workbook View protect underlying data?
Not on its own. Published data sources, downloads, extracts, database credentials, APIs and row-level security may create additional access paths. Review the complete data journey and test it using representative identities.
9. How should Tableau permissions work for embedded dashboards?
The embedding application should authenticate users appropriately and ensure Tableau identity and entitlements enforce the intended audience. Test direct links, session behavior, copied URLs, downloads and any service-account-based integrations.
10. What should be audited regularly?
Review privileged roles, group memberships, production project lock settings, user-specific exceptions, download capabilities, orphaned assets, published data-source access and sensitive content. Include both actual access and the evidence supporting it.
11. Can project leaders replace site administrators?
Project leaders can administer content in their applicable project hierarchy and are useful for delegated governance. They do not replace administrators for site-wide settings, identity management or platform operations.
12. How long does a Tableau permissions redesign take?
A limited pilot can often be structured over several weeks, but enterprise migration depends on the number of projects, existing exceptions, identity integration, data sensitivity and business testing. Estimate from an inventory rather than promising a universal timeline.
Conclusion: make access a reusable architecture
Tableau permissions scale when business audiences map cleanly to groups, governed content lives in deliberate projects and production access can be verified without tracing individual workbook exceptions. The result is not only a more secure reporting environment; it is a simpler operating model for onboarding, publishing, audits and organizational change.
For organizations reviewing a wider reporting estate, Actiknow’s business intelligence implementation and consulting services cover Tableau, data integration, modeling and dashboard delivery. Teams standardizing governed content can also review its custom business intelligence dashboards capabilities. If you are planning a permissions redesign or need a second opinion on a Tableau governance model, discuss your Tableau access model with Actiknow.
Editorial note: Platform behavior and available capabilities can vary by Tableau deployment, site settings and release. Validate the final permission design against your environment and current Tableau documentation before applying production changes.