
The real question is not whether to automate, but where to retain judgment
A workflow that processes every request automatically may look efficient until it approves an incorrect payment, changes a regulated record, or grants access to the wrong person. Conversely, requiring approval for every routine action can recreate the queue the automation was intended to remove. The objective of human-in-the-loop automation is to automate repeatable work while reserving consequential, ambiguous, or irreversible decisions for accountable people.
A human checkpoint is not a generic ‘Are you sure?’ screen. It is a designed control with a trigger, a named decision owner, the evidence needed to decide, a response deadline, a fallback, and an auditable outcome. Operations leaders should decide those elements before choosing workflow software.
Start with the decision, not the department
Map a process into individual decisions and actions. An invoice workflow, for example, may ingest a document, extract fields, match a purchase order, check vendor identity, detect duplicates, determine tax treatment, schedule payment, and release funds. Each step has different failure modes. OCR extraction can be retried; an incorrect payment may require a difficult recovery. The appropriate approval boundary therefore differs by step.
For every decision, document its business purpose, input quality, expected volume, permissible outcomes, potential loss, reversibility, regulatory constraints, and who can authorize an exception. Also identify which actions merely prepare a recommendation and which actions change an external system. This distinction often reveals a safe automation path: gather and validate automatically, then pause immediately before a consequential write.
A practical five-factor approval framework
1. Impact: what happens if the decision is wrong?
Assess financial exposure, customer harm, operational disruption, legal obligations, privacy consequences, and reputational risk. Do not use transaction amount as the sole proxy. A low-value request could expose sensitive information; a high-value transaction may be routine when it matches a previously approved contract and clear policy. Define impact bands with the business owner, not an arbitrary technology-team threshold.
2. Reversibility: can the outcome be safely undone?
Drafting an internal report is usually reversible. Sending a customer notification, deleting records, provisioning privileged access, and transmitting a payment may not be. For hard-to-reverse actions, place approval before the external effect. For reversible actions, consider automatic execution with monitoring, sampling, and a defined correction path.
3. Evidence quality: how certain are the inputs?
A rule-based match against authoritative records can be more dependable than a model-generated classification. Confidence scores are useful only when calibrated against representative outcomes; a score of 0.95 is not automatically a 95% probability of correctness. Missing documents, contradictory source values, unusual combinations, and unverified identities should trigger review or a request for more information.
4. Policy clarity: is the decision actually specified?
Automation should implement approved business policy, not invent it. If two experienced reviewers routinely disagree, investigate the policy before building the workflow. Route genuinely discretionary judgments to authorized people, and record the rationale so recurring ambiguity can eventually be resolved into clearer rules.
5. Accountability: who owns the outcome?
A human approval is meaningful only when the reviewer has authority, context, and time. Separate requesters from approvers where segregation of duties is required. Define delegation for absences, escalation for overdue requests, and secondary review for unusually sensitive actions. A shared inbox with no explicit owner is not a reliable control.
Choose among four operating patterns
Straight-through processing for low-risk, well-defined cases
Use automatic execution when inputs are validated, the rule is explicit, the action is within approved limits, and errors can be detected and corrected. Examples include routing a complete request to the correct team or updating an internal non-sensitive status from an authoritative event. Retain event logs and monitor exceptions even when no person approves each item.
Exception-based review for unusual cases
Process ordinary cases automatically, but pause when a validation fails, a duplicate is suspected, a threshold is crossed, or source systems disagree. The exception should contain the specific reason and relevant evidence. A reviewer should not have to reconstruct the entire transaction from raw logs.
Pre-action approval for high-consequence changes
Require an explicit decision before payment release, privileged access, sensitive data disclosure, destructive changes, or other actions defined as high risk. Approval must be bound to the exact proposed action and its version. If the amount, recipient, destination, or scope changes after approval, invalidate the authorization and request a new one.
Post-action sampling for reversible, high-volume work
Where individual approval would create disproportionate delay, use risk-weighted sampling, periodic audits, anomaly detection, and rapid correction. Sampling does not replace legally required approvals or controls. Increase sampling when error rates rise or a rule changes, and decrease it only with evidence of sustained quality.
Example: design an invoice approval workflow
Consider an illustrative company that receives invoices through email and a supplier portal. The system extracts invoice data, validates supplier and purchase-order identifiers, checks for duplicates, compares line items to the purchase order, and routes exceptions. These are design examples, not reported Actiknow client results.
Case A: An invoice has a recognized supplier, valid purchase order, exact three-way match where required, no duplicate indicators, and falls within a preapproved spending policy. The workflow can prepare it for the next authorized step, or process it automatically if the organization’s finance policy permits.
Case B: The invoice amount differs from the purchase order or bank details have changed. The workflow pauses, highlights the discrepancy, and requires review by the appropriate procurement or finance owner. A bank-account change may also require independent verification through a trusted channel, rather than relying on details in the invoice itself.
Case C: The invoice is urgent but lacks supporting documents. The workflow requests missing evidence and escalates according to a documented deadline. Urgency alone must not override mandatory controls. If a policy exception is allowed, it should be recorded with the approving authority and reason.
This pattern separates extraction and validation from authorization. It also creates useful analytics: the percentage processed without intervention, common exception reasons, review time, rework rate, and downstream corrections.
Design the approval experience as carefully as the automation
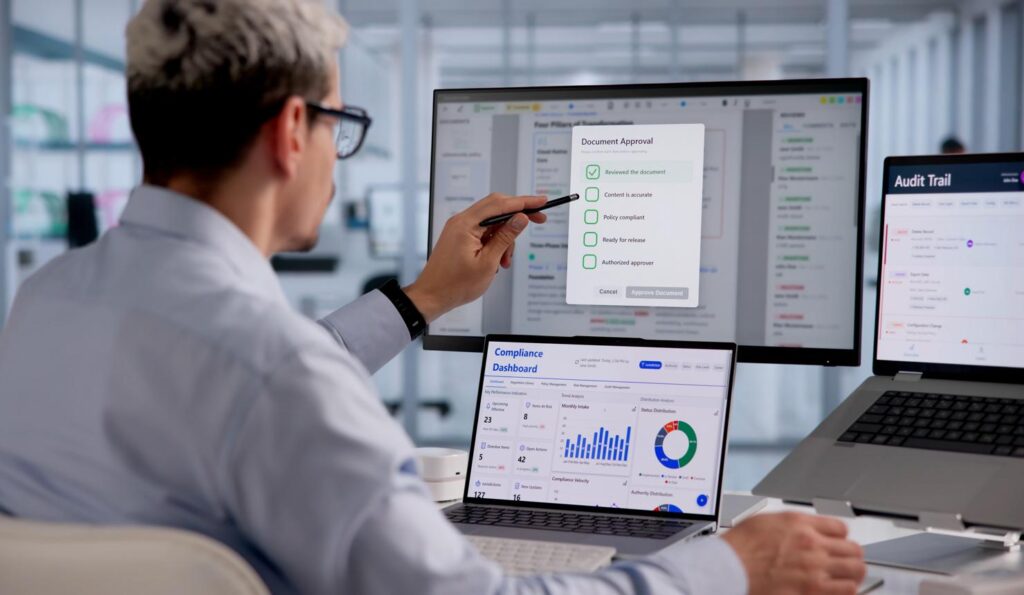
A reviewer needs a concise decision packet: request ID, requester, proposed action, source-of-truth fields, discrepancies, policy rule, impact, deadline, and links to supporting evidence. Show what changed since the last approval. Provide approve, reject, request information, and escalate actions when appropriate; avoid ambiguous ‘complete’ buttons that conflate reviewing with executing.
Use role-based access controls, least privilege, and clear separation of duties. Record the reviewer identity, decision timestamp, evidence version, policy version, reason, and resulting system action. Audit records should be tamper-resistant within the organization’s retention and privacy requirements. Approval by email or chat can be convenient, but the underlying service must authenticate the actor and bind the response to the correct transaction.
For workflows spanning APIs and business applications, Actiknow’s custom software and integration services provide a relevant starting point for understanding how application logic, user interfaces, and connected systems fit together.
Build for delays, retries, and changing information
A workflow may wait hours or days for a decision. Model waiting as a durable state, not an open web request or a background process held in memory. Persist the proposed action, its evidence snapshot, version, owner, and deadline. Use idempotency keys to prevent double execution when an approval message or API callback is retried.
Before execution, revalidate conditions that can change: account status, available balance, policy limits, permissions, record version, and the intended recipient. If the material facts changed, return to review rather than executing stale approval. Define what happens if the reviewer leaves, the approval expires, or an external system is unavailable. Expiration should not silently become approval.
For parallel approvals, specify whether all, any one, or a quorum must approve. Enforce required sequencing where relevant. Do not treat two approvals from the same person under different roles as independent if policy requires separation.
What operations teams should measure after go-live
Measure both speed and control effectiveness. Useful metrics include straight-through processing rate, exception rate by reason, median and 95th-percentile approval wait, overdue queue age, escalation frequency, rejection and rework rates, approval reversals, unauthorized-action incidents, and cost per correctly completed transaction.
Define denominators carefully. A 98% approval completion rate is misleading if unresolved requests disappear from the report. Track all eligible cases, including pending, expired, canceled, retried, and failed actions. Separate system processing time from human waiting time and from the time required to obtain missing evidence.
Review false positives (safe cases unnecessarily routed to people) and false negatives (risky cases that bypassed review). False negatives often matter more, but measuring them requires audits of some automatically processed cases. Build a feedback loop: investigate exceptions, revise approved rules, test against historical examples, and deploy changes with version control.
A 30-day implementation approach
Week 1: inventory decisions and classify risk
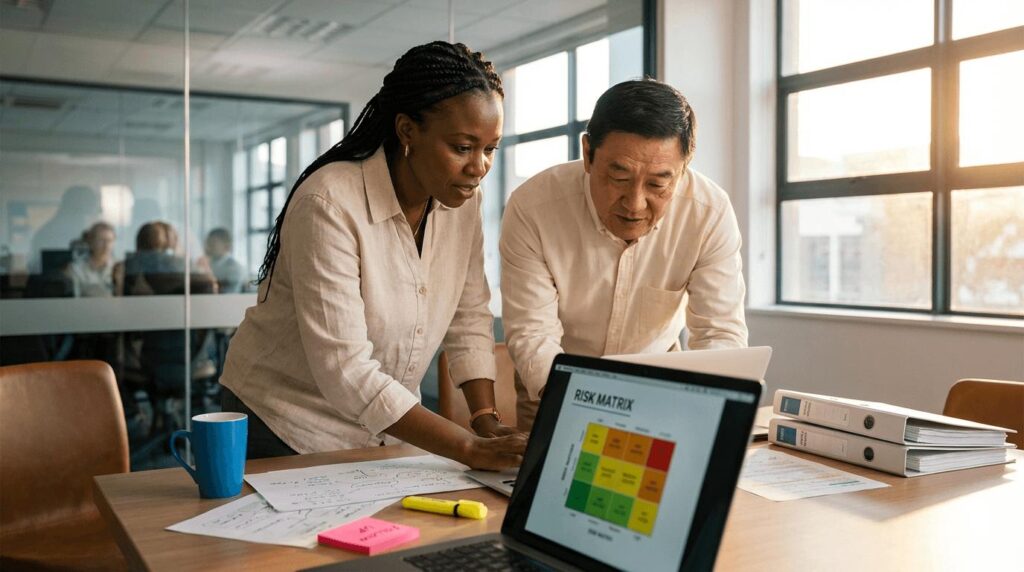
Select one workflow with measurable volume and a clear owner. Map its actions and identify irreversible effects, regulatory requirements, existing approval policies, and recurring exceptions. Agree on a risk matrix and an explicit list of actions that cannot proceed without authorization.
Week 2: define controls and reviewer journeys
Write decision rules, evidence requirements, reviewer roles, escalation deadlines, delegation policy, and audit fields. Prototype the decision packet with actual operational users. Test whether they can make an informed decision without opening five unrelated systems.
Week 3: build and test the state machine
Implement durable pending states, version checks, authentication, retries, idempotency, and error handling. Test changed data after approval, duplicate callbacks, reviewer absence, conflicting decisions, revoked access, expired approvals, and downstream API failures. Include negative tests proving that prohibited actions cannot bypass the checkpoint.
Week 4: launch with evidence and tune
Start with a limited group or transaction class. Compare automated decisions to established policy, monitor the queue daily, and review sampled straight-through cases. Set explicit expansion criteria based on error rates, backlog, reviewer burden, and business outcomes rather than the number of tasks automated.
Executive approval-design checklist
Before launch, ask:
- Are high-impact and irreversible actions identified?
- Is every checkpoint tied to a specific policy and authorized role?
- Can a reviewer see the exact action and evidence?
- Are changed facts revalidated before execution?
- Are duplicate approvals harmless?
- Is there a documented path for timeout, absence, and disagreement?
- Can the organization demonstrate who approved what, when, and why?
- Are false negatives audited as well as approval queues?
If the answer to any of these is unclear, the workflow may be technically functional without being operationally controlled.
Frequently asked questions
What does human-in-the-loop automation mean?
It means automated systems perform defined tasks while people review selected decisions or exceptions. The checkpoint should be triggered by business risk or uncertainty, not inserted indiscriminately.
Should every AI-generated decision require approval?
Not necessarily. The required control depends on the action’s impact, input quality, reversibility, and applicable policy. A generated internal draft differs materially from a decision that releases money or changes access rights.
How do we set approval thresholds?
Use historical transaction distributions, incident severity, financial exposure, policy obligations, and operational capacity. Validate thresholds with process owners and test borderline cases. Revisit them as volumes and risks change.
Can confidence scores determine when a human is needed?
They can be one signal if calibrated and monitored. They should not override mandatory controls or substitute for checks on missing evidence, inconsistent records, or irreversible consequences.
What if an approver does not respond?
Use defined deadlines, reminders, delegated approvers, and escalation. High-risk requests should normally remain pending or fail safely rather than automatically approve on timeout.
Can approvals happen in email or messaging apps?
Yes, provided the action authenticates the reviewer, confirms authority, binds the decision to a specific versioned request, and creates a durable audit record. A forwarded message alone is not sufficient authorization.
How do we avoid an approval bottleneck?
Automate low-risk cases, route only meaningful exceptions, show concise evidence, set service-level targets, and analyze recurring exception causes. Remove unnecessary checkpoints only after demonstrating acceptable control performance.
What is the difference between human-in-the-loop and human-on-the-loop?
Human-in-the-loop requires a person to decide at specified points before progression. Human-on-the-loop generally means people supervise a running process and intervene when necessary. Both require clear authority and monitoring.
How should approval history be retained?
Retain identity, timestamp, request and policy versions, evidence references, decision reason, and execution result according to applicable legal, privacy, and organizational retention rules. Limit access to sensitive records.
How do we know the design is working?
Measure correct completion, harmful bypasses, queue age, review burden, exception patterns, and downstream corrections. An automation rate alone cannot demonstrate safety or business value.
Make approval a designed control, not an afterthought
The strongest automation programs do not attempt to remove people from every decision. They make routine work faster, concentrate human attention where it changes outcomes, and preserve evidence when judgment matters. Start with the consequences of each action, build explicit approval boundaries, and improve them using operational data.
If your team is designing a workflow that spans approvals, business rules, and multiple systems, discuss the requirements with Actiknow through its contact page. A focused discovery conversation can help define the workflow, integrations, and controls before implementation.