
A restored database is not necessarily a recovered business service. Tables may be present, yet analysts cannot query them, scheduled transformations fail, or sensitive information becomes available to the wrong people. That is why access design belongs in the recovery plan, not in a separate security document that nobody opens during an incident.
Snowflake’s September 18, 2026 update changed an important limitation: schema and database backups can now include database roles. Previously, a backup could fail when its scope included a database role or an object whose ownership was granted to a database role. This removes a material obstacle for teams that organize privileges around database-scoped roles. It does not mean every grant, user entitlement, integration or downstream dependency will be reconstructed automatically.
The executive question is simple: after restoring data, can the right people and applications perform the right work, without granting broader access than before?
What changed in September 2026
Snowflake’s release note states that database roles can now be included in schema and database backups. Database roles are scoped to a database and can be granted to account roles; users activate account roles, not database roles directly. That distinction matters during recovery because restoring the database-side role definition is not the same as confirming that the account-level role hierarchy and user assignments are correct.
The broader Snowflake backup documentation lists database roles, supported grants, masking policies, row access policies and several other objects among backup-supported elements. It also identifies important exclusions. Backups are not universal copies of an account. Teams should read the current supported-object matrix for their backup scope and edition before relying on a restore.
For data leaders, the practical improvement is that a database with deliberately designed database roles is easier to include in a recovery strategy. The remaining challenge is to validate the complete authorization path.
Why data recovery and access recovery are different
Consider a reporting database containing customer orders, finance aggregates and operational metrics. The database might have a reader role for dashboards, a transformation role for scheduled models and a restricted role for sensitive financial tables. A backup could preserve data and eligible database roles, but successful operations also depend on account roles, role grants, service identities, warehouses, connections, secrets, external integrations and application configuration.
Three distinct outcomes need testing. First, data integrity: are the expected objects and records present? Second, functional continuity: do pipelines and dashboards actually run? Third, authorization integrity: are permissions no broader or narrower than the approved baseline?
Passing only the first test can create a false sense of readiness. A dashboard that cannot read its tables is an outage. A dashboard that can suddenly read restricted data is a security incident.
Understand the two layers of Snowflake roles
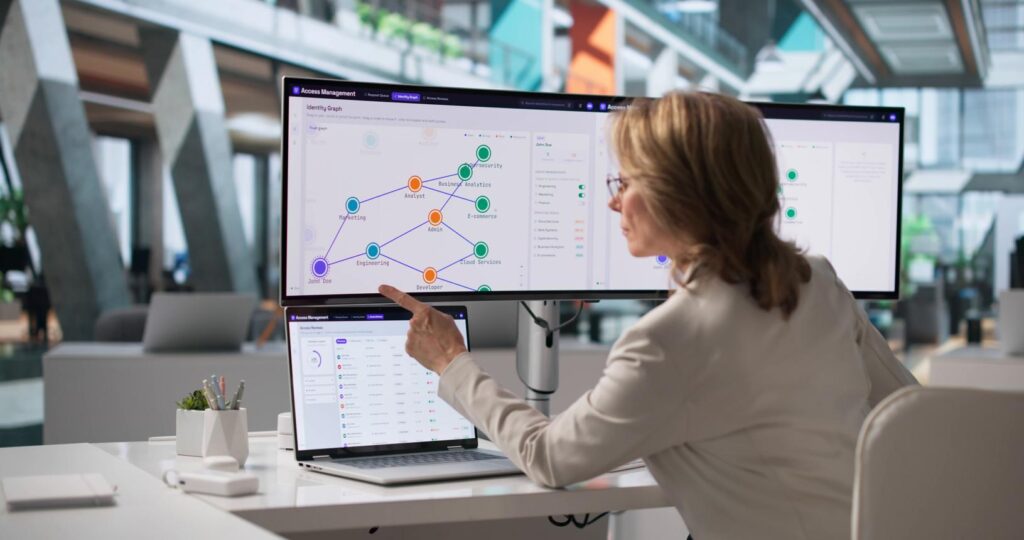
Database roles bundle privileges on objects within a database. Account roles can inherit database roles and are assigned to users or service principals. This allows database teams to define reusable access packages while security teams control who receives them.
For example, SALES_DB might define SALES_DB.REPORTING_READER and SALES_DB.PIPELINE_WRITER. An account role such as BI_PRODUCTION could inherit the reader database role. A separate application account role could inherit the writer role. These names are illustrative, not a recommended universal hierarchy.
A recovery runbook should record the database roles, their object grants, ownership assignments, account-role inheritance, user or service-principal assignments and any dependencies outside the backup. Store this baseline securely, version it and review it whenever the role model changes.
Ownership requires special attention
Snowflake’s backup documentation cautions that grants on restored objects can differ from the original grants. In particular, dropping a role transfers associated ownership grants to the role performing the drop, while non-ownership grants associated with that role are deleted. Consequently, a restored object’s privileges may not precisely match those at backup creation.
Do not assume a successful restore command proves ownership fidelity. Compare object ownership and effective access with a pre-incident baseline. Where restoration requires changes, document the approving security owner and the least-privilege corrective action.
What is actually covered by the backup?
Snowflake supports database and schema backups with a documented matrix of included and excluded object types. Supported objects can include tables, views, database roles, tasks and certain policies, subject to the specific rules described in the documentation. Tasks restored from backup are suspended and must be resumed intentionally after validation.
Not everything is covered. Snowflake’s documentation identifies exclusions including streams, pipes, external stages, certain policy types, semantic views and other account or application resources. A team relying on those elements needs separate recreation or recovery procedures.
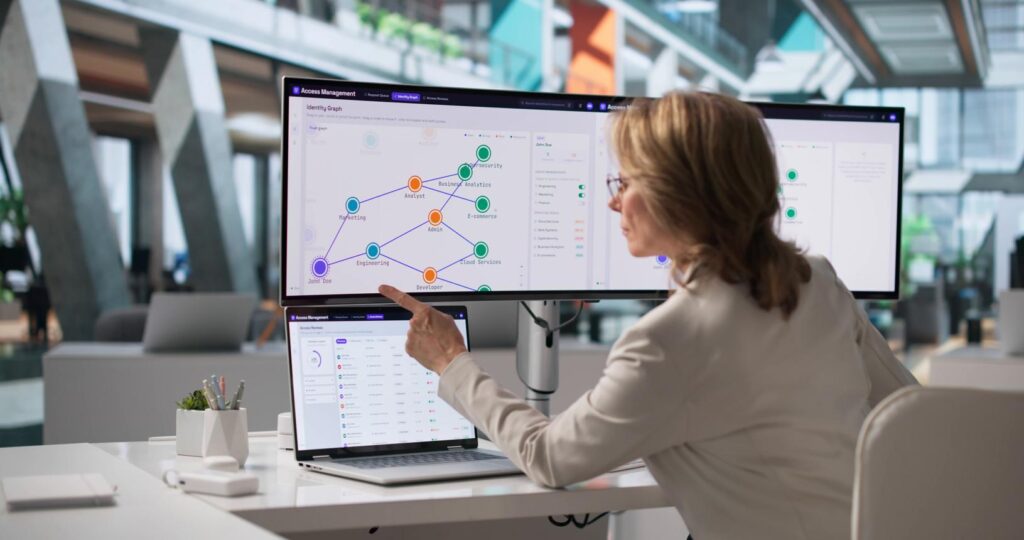
The right design is therefore a dependency map, not merely a list of backed-up tables. For each critical reporting product, identify its data, role hierarchy, orchestration, ingestion, transformations, warehouse access, network requirements and consuming applications. Mark which dependencies the backup restores, which require infrastructure-as-code and which need manual approval.
A practical recovery access matrix
Create one row per business capability, not just per Snowflake object. Useful columns include business service, database and schema, critical object, required database role, inheriting account role, principal or service, permitted action, sensitivity classification, restore validation owner and test evidence.
For a finance dashboard, the expected action may be SELECT on a governed mart, with no access to raw payroll data. For a transformation service, the expected actions may include reading staging tables and writing a specific reporting schema. For an audit reviewer, the expected action may be read-only access to designated compliance evidence.
Include negative tests. Confirm that a marketing analyst cannot query restricted payroll tables and that a pipeline identity cannot modify security policies. Recovery is successful only when allowed actions work and prohibited actions remain prohibited.
The seven-step restore validation sequence
- Establish the approved baseline. Export or document database roles, account-role grants, object ownership, policy attachments and application dependencies before an incident. Use a controlled source of truth rather than screenshots alone.
- Select the recovery point and environment. Confirm the backup’s age, scope, retention constraints and destination. Avoid conducting first-time recovery experiments in the production namespace.
- Restore the supported database or schema objects. Follow Snowflake’s current restore procedure and check the operation result. Record the restore identifier, timestamps, operator and change ticket.
- Inventory restored roles and objects. Compare expected database roles, schema objects and security policies with the baseline. Investigate missing or renamed objects before opening access to consumers.
- Reconnect account-level permissions deliberately. Validate the inheritance chain between restored database roles and account roles. Re-establish only approved grants where needed; do not use broad administrator access as a permanent workaround.
- Run positive and negative authorization tests. Execute representative queries as the actual application or user roles. Confirm restricted tables remain restricted, masking and row access behavior matches expectations, and service identities can perform their required operations.
- Restart dependent services in stages. Verify upstream ingestion, transformation jobs and dashboards. Remember that restored tasks are suspended. Resume only after prerequisites, security checks and business reconciliations pass.
Each step should have a named owner, an expected result and an escalation path. The sequence is a planning template; production procedures must reflect the organization’s actual Snowflake edition, backup configuration and compliance obligations.
Recovery objectives must include permissions
Recovery point objective (RPO) describes the maximum acceptable data loss measured in time. Recovery time objective (RTO) describes the target duration for restoring service. Neither metric should stop at the moment the data objects reappear.
Measure time to usable, authorized service. This includes restoring required access, validating policies and re-enabling critical workloads. Track the proportion of required authorization tests passed, the number of unauthorized-access findings and the time needed to resolve permission mismatches.
For a board-level scorecard, report the last successful restore test, actual recovery duration, data freshness at recovery, critical services validated, access exceptions and open remediation actions. Avoid claiming that a backup schedule alone proves recovery readiness.
Least privilege during an incident
Disaster recovery creates pressure to grant sweeping permissions quickly. That can leave long-lived exceptions after the incident. Use preapproved break-glass roles with documented activation conditions, short-lived access where feasible, logging and post-incident review.
Separate the person executing the restore from the person approving sensitive access changes when practical. Require a security sign-off before reconnecting high-risk workloads. Any temporary elevation should have a clear expiration and owner.
Also consider restored data in a non-production environment. A test restore containing production personal or financial information still needs controls appropriate to its sensitivity. A technically isolated database is not automatically a safe testing environment.
How to test the feature without disrupting production
Start with a small, representative database that uses database roles and contains ordinary objects plus the policies your business relies on. Create a supported backup using a correctly authorized role. Restore to a controlled destination and compare role inventory, ownership and effective permissions.
Test at least one permitted read, one permitted write where relevant, one prohibited read, one masking or row-access behavior, and one downstream application connection. Repeat after changing a role grant to ensure the recovery baseline stays current.
Keep the test results in an evidence register: test date, backup scope, restore location, role tested, expected outcome, observed outcome, exceptions and remediation owner. Do not treat a single successful dry run as permanent proof. Re-test after meaningful changes to role hierarchy, object types, policies or critical integrations.
Common mistakes to avoid
Mistake one: equating role inclusion with complete identity recovery. Database roles are only part of the authorization chain.
Mistake two: validating access as ACCOUNTADMIN. Administrator success does not demonstrate that actual business roles work.
Mistake three: restoring tasks and immediately enabling everything. Restored tasks are suspended for a reason; dependent systems and permissions should be checked before resumption.
Mistake four: ignoring unsupported objects. A backup may restore tables while a missing stream or pipe prevents the data from updating.
Mistake five: failing to test denial. A role that can query too much is just as important as a role that cannot query enough.
Mistake six: not maintaining the baseline. Without a reliable pre-incident inventory, teams cannot confidently distinguish legitimate differences from accidental privilege drift.
A 30-day implementation plan
Week 1
Classify critical data products and their access dependencies. Identify the database roles, account roles, ownership grants, policies and external components supporting each service. Assign business and security owners.
Week 2
Review Snowflake backup scope, permissions, retention and supported-object limitations. Build a role-to-service matrix and document the restore sequence. Identify missing infrastructure-as-code coverage.
Week 3
Conduct a controlled restore exercise. Capture positive and negative access tests, object reconciliation, task state and application-level checks. Record recovery duration and any privilege mismatches.
Week 4
Remediate gaps, approve the runbook, set a recurring exercise cadence and add recovery-access measures to operational reporting. Update the plan when the role model or Snowflake feature behavior changes.
Executive acceptance checklist
A recovery plan is ready for approval when the team can answer these questions with evidence:
- Which business services are covered?
- Which objects are excluded?
- Which database roles are restored?
- How are account roles and service identities reconnected?
- Who approves privilege changes?
- Are masking and row access policies verified?
- Have both permitted and denied operations been tested?
- Are restored tasks restarted safely?
- Can the team demonstrate an end-to-end RTO and RPO?
- Is there a dated, reviewed test record?
If any answer is unknown, the organization has a recovery design gap rather than a mere documentation gap.
Frequently asked questions
Does Snowflake now back up database roles?
Yes. Snowflake announced support for including database roles in schema and database backups on September 18, 2026. Check the current documentation for scope and limitations.
Does restoring a database role restore all user permissions?
No. Effective access also depends on account-role inheritance, user or service assignments and other account-level configurations. Validate the entire chain.
Are grants guaranteed to be identical after a restore?
Do not assume so. Snowflake documents circumstances in which grants on restored objects can differ, including role deletion and ownership-transfer behavior.
Can a backup replace infrastructure-as-code?
No. Backups and version-controlled configuration serve different purposes. Configuration remains important for account-level dependencies and excluded objects.
Are tasks immediately active after a restore?
No. Snowflake documents that tasks restored from backups are suspended and must be resumed intentionally.
Should we restore production data into development for testing?
Only with appropriate authorization, isolation and data protection. Production data sensitivity does not disappear because the destination is non-production.
What should the security team validate?
Role inheritance, object ownership, effective grants, policy behavior, service identities, prohibited access and any temporary elevated privileges.
What is the most useful recovery metric?
Time to a functioning and correctly authorized business service, alongside RPO, authorization test pass rate and unresolved access exceptions.
How often should restore tests run?
Choose a cadence based on business criticality and change frequency. Re-test after major permission, policy, architecture or workload changes.
Does database-role backup support remove the need for a runbook?
No. It makes one part of recovery more complete, but sequencing, approvals, excluded objects, integrations and verification still require a tested procedure.
Conclusion: recover trust, not just tables
Snowflake’s database-role backup enhancement is useful because permissions are part of what makes data operational. But it should be treated as an opportunity to strengthen recovery assurance, not as a promise that every identity and dependency will return automatically.
Organizations evaluating their data platform’s resilience can combine role-aware recovery testing with a broader BI architecture review. Actiknow’s business intelligence consulting and implementation services cover data integration, modeling and reporting. If your team needs help assessing reporting dependencies or planning a more reliable analytics environment, contact Actiknow to discuss the requirements.
Sources and further reading
Snowflake release note: September 18, 2026 database roles in backups
Snowflake documentation: Backups for disaster recovery and immutable storage