
An executive decision guide to sign-in methods, security, account recovery and lifecycle management for consumer and enterprise mobile products.
The login screen is a product decision, not just an engineering task
A user opens a new mobile application. Should the first screen ask for an email and password, offer Google or Apple sign-in, or redirect to the user’s employer? That choice shapes onboarding, support costs, security exposure, data ownership and the product’s ability to serve enterprise customers.
Teams often choose whichever SDK is easiest to implement for an MVP. Later, the product needs corporate single sign-on, contractor access, account linking, multi-factor authentication or a way to remove a departing employee immediately. Retrofitting these capabilities can be much harder than designing the identity model before launch.
There is no universally best sign-in button. A consumer marketplace, employee field tool, B2B customer portal and financial workflow serve different users. The decision should begin with who controls each identity, what access it permits and what happens when the user loses a phone, changes employer or switches sign-in providers.
Authentication should be designed with the wider application architecture. Actiknow’s cross-platform mobile app development services cover the mobile product lifecycle, while the choices below explain what product owners should require of the identity layer.
Five questions to answer before choosing a provider
- Who will sign in? Distinguish consumers, employees, contractors, customer administrators, guest users and support personnel. A single application may need different methods for different groups.
- Who owns the identity? A consumer controls a personal account; an enterprise may control its employees’ accounts. Your application should still control its own internal user records, organization memberships and business permissions.
- What is the impact of account takeover? Reading general content differs from changing payment details, exporting sensitive records or approving financial transactions. Classify actions by risk rather than applying identical controls everywhere.
- How will access end? Plan for employment termination, customer cancellation, account compromise, revoked social credentials, device loss and account deletion. Offboarding is part of authentication architecture.
- Where must the app work? Consider iOS, Android, managed devices, shared tablets, limited connectivity, personal devices and enterprise restrictions. A flow that works in a developer’s browser may fail in a managed mobile environment.
The four authentication options and their trade-offs
1. Email and password: control with continuing responsibility
A first-party password account gives the product broad control over registration, branding and account policy. It does not require users to have an existing social or corporate identity. This can be useful for specialized audiences, independent contractors and products that need a portable first-party account.
But passwords create operational work. The system must protect credentials, prevent automated abuse, handle resets, detect suspicious activity and provide recovery when email is unavailable. Credential stuffing and phishing remain risks even when passwords are stored correctly.
Use a mature identity platform rather than implementing password hashing and reset infrastructure from scratch. Require modern password storage, rate limiting, secure recovery, appropriate breached-password checks and MFA or passkey enrollment where risk justifies it. Do not introduce arbitrary frequent password changes without a clear policy reason.
The executive question is not whether a password form can be built quickly. It is whether the organization is prepared to operate password authentication safely for years.
2. Social login: convenient onboarding with provider dependency
Social sign-in allows users to authenticate with an existing account, commonly Apple or Google. It can reduce registration friction and remove the need for another password. This often fits consumer products where conversion and repeat access matter.
The provider, however, does not own your application’s permissions. A successful Google login should not automatically grant access to purchases, workspaces or administrator functions. The backend must map the provider identity to a durable internal user and enforce entitlements independently.
There are also support cases: the user loses access to a social account, a provider returns a private email address, a person has two provider accounts, or a social provider is unavailable. Offer appropriate alternatives and account recovery. Do not treat matching email strings as proof that two accounts belong to the same person.
For iOS products, social login also intersects with platform review rules. Check those rules during product design, not just before submission.
3. Enterprise SSO: organization-managed identity and access
Enterprise single sign-on allows employees and B2B customer users to authenticate through an organization-managed identity provider, such as Microsoft Entra ID or another standards-based service. It can let the customer apply its own MFA, conditional access and account policies.
For B2B software, SSO may be an explicit procurement requirement. A customer may expect domain verification, tenant-specific connections, role mapping, provisioning, audit logs and prompt offboarding. The app must also decide how guests and contractors access the same organization.
SSO is not a single checkbox. A product may need OpenID Connect for modern identity integrations, SAML for existing customer environments, and a documented process for certificate rotation and configuration changes. Use supported libraries rather than hand-built token parsing. Microsoft’s authorization code with PKCE guidance describes a supported pattern for mobile clients.
An SSO demonstration proves that login works. It does not prove that terminated employees lose access, cached sessions expire correctly or tenant data remains isolated.
4. Passkeys: stronger authentication without reusable passwords
Passkeys use public-key cryptography. A user can authenticate by unlocking a credential through a device PIN or biometric mechanism, while the server verifies a cryptographic response. This reduces dependence on reusable passwords and can provide phishing-resistant sign-in.
Passkeys do not remove the need for an account model, permissions or support. A user may lose all devices, change ecosystems, use an enterprise-managed phone that restricts syncing, or need to recover from a shared workstation. Those scenarios need designed, tested paths.
A weak recovery process can undermine a strong primary method. Do not let someone bypass a passkey simply by persuading support to change an email address. Android’s Credential Manager passkey documentation explains the server challenge and public-key verification responsibilities.
Passkeys can complement social login or first-party accounts. The product should decide whether to make them primary, optional or required for certain high-risk populations.
A practical decision matrix
Passwords are a reasonable choice when broad first-party account control is essential. Their main cost is ongoing credential protection, abuse prevention and recovery. They should not be selected solely because they are familiar.
Social login is often suitable for consumer onboarding and frequent repeat visits. Its main risks are provider dependency, limited user control over provider access and unsafe account linking. It needs a fallback and a durable application identity.
Enterprise SSO is appropriate when an organization must govern employee or customer access. Its main complexity lies in tenant configuration, provisioning, role mapping and offboarding. The customer’s identity provider authenticates; the application still authorizes.
Passkeys are attractive when convenient, phishing-resistant sign-in is supported by the user environment. Their main challenges are enrollment, cross-device use and secure recovery. They are an authentication mechanism, not an entire user-management platform.
These options are not mutually exclusive. A consumer app might offer social sign-in and passkeys. A B2B SaaS platform might use enterprise SSO for larger customers and controlled invitation-based access for smaller accounts. The objective is a coherent identity architecture behind carefully chosen entry points.
Authentication asks: has this person proved control of an accepted credential? Identity management asks: which application account does that credential belong to? Authorization asks: what may this account do, in which tenant, workspace or project?
These are different questions. A valid social or enterprise token must not automatically imply administrator access. The backend should validate the token, resolve the external identity to an internal user, identify the active organization and enforce permissions for every protected request.
Create a durable internal user ID that survives email changes. Store external identities as mappings using the issuer and stable subject identifier, not merely the email address. Keep roles and organization memberships separate. This makes it possible to support multiple providers and change identity vendors without rewriting business data.
For multi-tenant products, verify membership and resource ownership server-side. Never accept a tenant ID supplied by the mobile client as proof that the user belongs to that tenant. A person may have different roles in different customer organizations.
The secure native mobile login pattern
A mobile app is a public client. A secret embedded in the app package can be extracted, so it should not be treated as a confidential server-side credential.
For standards-based native sign-in, use authorization code with Proof Key for Code Exchange (PKCE) and an external browser or secure browser tab. Register redirects carefully and validate protocol parameters. The IETF’s OAuth 2.0 for Native Apps standard requires external user agents and PKCE for public native clients.
Avoid embedded web views that let the application inspect a provider’s login page. Validate issuer, audience, signature, expiry and relevant state or nonce values according to the protocol. Use maintained platform libraries wherever possible.
OpenID Connect adds an identity layer to OAuth. An ID token provides authentication claims for the intended client; an access token authorizes access to a specific API. Do not substitute one for the other or treat any signed token as valid for every backend service.
Use short-lived access tokens, carefully managed refresh credentials where necessary, platform secure storage and server-side revocation. Never log passwords, bearer tokens or recovery secrets. A fingerprint prompt can protect a local credential, but it does not replace backend authorization.
Account linking: the overlooked source of account takeover
Imagine a user signs up with email and password, later chooses Sign in with Apple, then joins an employer that enables SSO. A poorly designed system may create three accounts, split the user’s history or merge identities incorrectly.
Do not merge accounts solely because their email addresses match. Providers can hide email addresses, corporate emails can be reassigned, and some claims may not be verified. Use the external provider’s issuer and stable subject identifier for mapping.
To link a new identity, require proof of control of the existing account and a fresh successful authentication with the new provider. Show which account will be linked. Notify the user when identity connections change and apply stronger verification for high-risk accounts.
Define unlinking rules. A user should not be allowed to remove the last usable authentication method without enrolling another. Keep an audit history and ensure support cannot bypass the linking process through an informal request.
MFA, step-up checks and sensitive actions
Not every action needs the same authentication assurance. Browsing a catalog may need an ordinary session. Changing bank details, exporting customer data, granting admin access or approving a high-value transaction may need recent reauthentication or a stronger factor.
For enterprise users, use the customer’s identity-provider controls where practical, but define application-level step-up for especially sensitive actions. For first-party accounts, choose risk-appropriate MFA and recovery. Avoid treating an SMS code as equivalent to phishing-resistant authentication.
NIST’s digital authentication guidance distinguishes assurance levels and phishing resistance. Manually entered one-time codes are not considered phishing-resistant because they can be relayed to an attacker’s session.
Create a policy table with each sensitive action, required assurance, maximum session age, permitted fallback and exception owner. This turns vague security expectations into requirements that engineering and QA can test.
Enterprise SSO must include provisioning and offboarding
The login demonstration is often the easiest part of SSO. Production questions begin afterward. Who creates the user record? Which group maps to a role? How quickly is access removed after termination? What happens to an active mobile session when an employee is disabled?
Evaluate SCIM or another supported provisioning mechanism for customers that need automated account lifecycle management. If automation is unavailable, define a documented reconciliation and deprovisioning process. Just-in-time account creation at first login does not solve account removal.
Keep each enterprise connection tenant-specific. Verify customer domains, protect configuration changes and test guest access, suspended tenants, certificate rotation, key changes and administrator lockout. Never trust unvalidated claims to assign powerful roles.
These decisions affect the backend and integration layer, not just mobile screens. Actiknow’s custom application and integration services describe the broader web, mobile and systems-integration work in which identity governance must fit.
Account recovery, device loss and offline access
A secure primary login is insufficient if a legitimate user cannot regain access after losing a phone. Define recovery separately for consumers, employees, customer administrators and privileged users. Enterprise employees may recover through their own identity provider; consumers may need alternative verified credentials.
Document acceptable recovery evidence, session revocation, user notifications and escalation for suspicious requests. For high-risk accounts, consider additional verification or review before changing a recovery method. Avoid error messages that reveal whether a particular email address has an account.
Test app reinstall, phone replacement, lost passkeys, disabled biometric unlock, inaccessible email, provider outage, revoked corporate access and multiple identities. A user who authenticates successfully but no longer belongs to the organization must still be denied its data.
Offline field apps require explicit rules. Decide what cached information may remain available, for how long, and whether it is encrypted. Define logout deletion and what happens when access was revoked while the device was offline. Recheck authorization before synchronizing sensitive changes.
Platform policies are part of product requirements
Apple’s current App Review Guideline 4.8 describes an equivalent privacy-preserving sign-in option for apps that use third-party or social login for the primary account, subject to exceptions such as qualifying enterprise and education applications. Read Apple’s App Review Guidelines for the actual rule rather than assuming every app must use the same set of buttons.
On Android, test credential and browser flows across supported versions and device policies. On both platforms, test canceled sign-ins, redirect handling, accessibility, provider outages, account deletion and sign-out. Shared cross-platform code does not eliminate platform-specific identity behavior.
Four product scenarios
Consumer subscription application
Favor low-friction registration through an appropriate mix of social sign-in, passkeys or first-party credentials. Tie subscription entitlements to the internal user ID. Test restoration on a new phone, duplicate accounts, canceled sign-in and changes in provider email. Do not force a social provider on users who cannot access it.
Employee field-operations application
Enterprise SSO is often the natural fit when the employer manages accounts and devices. Plan rapid offboarding, shared-device logout, offline retention, contractor invitations and conditional access. Avoid shared employee credentials, even when shifts change quickly.
Multi-tenant B2B customer application
Allow tenant-specific SSO where required, while retaining controlled access paths for smaller customers and external collaborators. Build organization-aware identity mapping, role assignment, admin recovery and provisioning before adding many enterprise connections. Test one person belonging to multiple customers.
Healthcare or financial workflow
Start with a threat model, data classification, regulatory analysis and audit requirements. Use stronger assurance for high-risk actions and enforce server-side authorization. A provider’s MFA feature or biometric unlock does not, by itself, establish regulatory compliance.
The total cost of ownership executives should compare
Do not compare only SDK implementation hours. Include identity-platform licensing, monthly active users, authentication volumes, SMS or email delivery, enterprise connection charges, MFA enrollment, recovery support, audit retention, security testing and vendor-policy changes.
Build a four-part cost model: implementation; recurring provider fees; internal operations and support; and change or incident costs. Ask vendors what happens when user count grows tenfold, enterprise tenants multiply or login traffic spikes during a campaign.
Confirm whether SSO, SCIM, custom domains, advanced audit logs and conditional access are included or priced separately. Check data portability and provider exit options. A durable internal identity model reduces lock-in without requiring you to operate your own identity server.
A six-week implementation roadmap
Week 1: Establish identity policy
Inventory user populations, device types, protected data, risk tiers and customer obligations. Identify the owners of authentication policy, support and security incidents. Produce a written decision record explaining which methods are offered to whom.
Week 2: Design accounts and permissions
Define internal user IDs, external identity mappings, organization memberships, role assignment, account linking, recovery, deletion and session lifetime. Draw the registration, sign-in, refresh, logout, revocation and offboarding journeys.
Weeks 3 and 4: Build a secure end-to-end slice
Implement one representative native sign-in flow with supported libraries, PKCE or passkey APIs as appropriate, protected token handling and backend authorization. Automate tests for invalid tokens, cross-tenant access, expired sessions and revoked users before expanding the interface.
Week 5: Test failures and edge cases
Exercise provider outages, lost devices, canceled browser returns, linked identities, stale claims, managed devices, offline access and admin lockout. Conduct a security review and confirm app-store requirements for the selected login options.
Week 6: Pilot and operationalize
Release to a small representative group. Measure sign-in completion, time to first successful session, recovery completion, repeated prompts, provider errors and support volume. Prepare support procedures and incident escalation before general release.
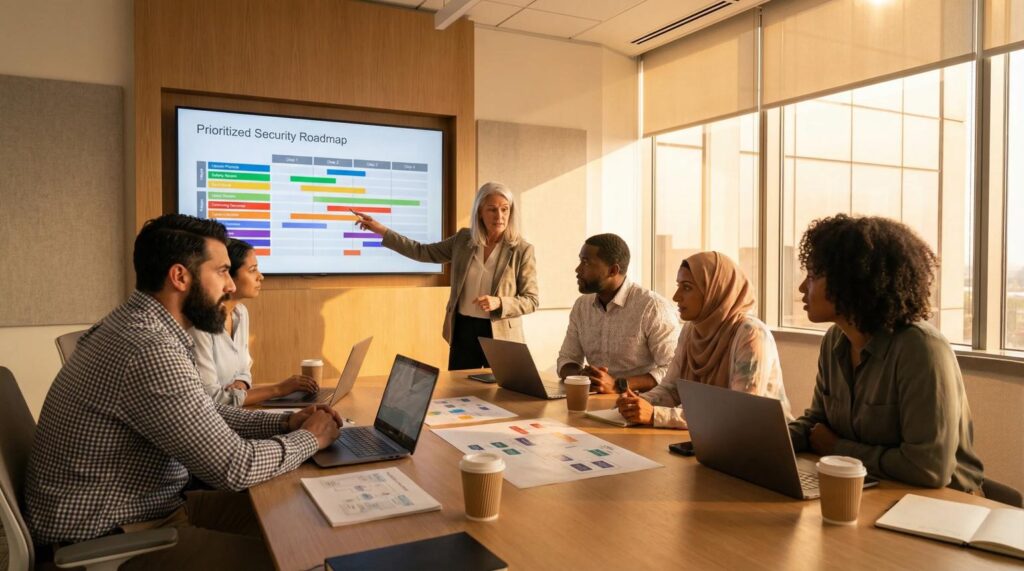
This sequence is illustrative, not a universal estimate. A single consumer login method may be simpler; multiple enterprise SSO connections or regulated workflows can require substantially longer validation and procurement.
Acceptance checklist before launch
Identity: every external login maps to the intended internal account; email changes do not orphan data; account linking requires verified control; duplicate-account resolution is documented.
Security: backend authorization is enforced; appropriate native browser and PKCE patterns are used; tokens are validated and protected; sessions can be revoked; sensitive actions have explicit step-up requirements.
Enterprise: tenant configurations are isolated; role mappings are tested; departing users lose access; administrators have a controlled recovery path; customer onboarding documentation is available.
Experience: cancellation and errors are understandable; alternative sign-in and recovery paths work; accessibility is tested; account deletion is supported; supported devices and app versions are covered.
Operations: audit events do not expose secrets; abnormal sign-in and recovery patterns can be investigated; provider outages are distinguishable from app failures; data retention and support ownership are defined.
What to measure after launch
Track sign-in completion by method, platform, app version and provider. Measure registration abandonment, median and slow-tail login time, recovery initiation and completion, MFA or passkey enrollment, repeated login prompts and support tickets per active user.
For enterprise deployments, monitor provisioning delay, deprovisioning delay, SSO configuration failures and role-mapping errors. For security, monitor unusual recovery activity, account-link changes, suspicious repeated failures, privilege changes and attempted reuse of revoked sessions.
Review product and security metrics together. A faster sign-in experience is not a win if account takeover, user confusion or administrative workload increases.
Frequently asked questions
It can reduce direct password-handling responsibility, but security depends on the provider, token validation, account linking and recovery. An insecure integration can still expose accounts.
Should a consumer app launch without passwords?
It can if the audience has accessible alternatives and recovery is robust. Test users who cannot or do not want to use the offered identity providers.
Is Sign in with Apple mandatory if we offer Google login?
Apple’s Guideline 4.8 sets requirements for covered social-login use cases and lists exceptions. Review the current guideline for your app and distribution model.
Yes. Keep one internal identity and authorization model, then enable approved sign-in methods by user type and tenant. Never silently merge accounts based on email.
Is SAML better than OpenID Connect for mobile apps?
Neither is universally better. OpenID Connect often suits modern native and API-based designs, while enterprise customers may have existing SAML requirements. Use maintained integrations.
Does SSO automatically remove terminated employees?
Not necessarily. Existing sessions, application membership and locally cached data still need revocation or expiry. Offboarding must be designed and tested.
Do passkeys eliminate the need for MFA?
A passkey can provide strong phishing-resistant authentication, but whether it meets a specific assurance requirement depends on implementation and policy. Some sensitive actions may need additional checks.
Can Face ID or fingerprint unlock replace backend authentication?
No. Biometrics can protect a local credential or session, but the server must still validate the session and enforce authorization.
How should a lost phone be handled?
Provide verified recovery appropriate to account risk, revoke compromised sessions where necessary and use stronger review for privileged accounts. Test the journey before launch.
Can email be the permanent user identifier?
Avoid it. Email addresses can change, be hidden or be reassigned. Use a durable internal user ID and map external identities by issuer and subject.
Lifecycle operations: recovery, abuse prevention, enterprise onboarding, offboarding, auditability, support and provider-policy changes.
What should a CTO approve before development begins?
Approve the user populations, identity ownership, risk tiers, supported methods, linking and recovery rules, tenant boundaries, costs and measurable acceptance criteria.
Passwords, social sign-in, passkeys and enterprise SSO solve different problems. A consumer app should not inherit enterprise complexity without a reason; a B2B product should not postpone identity governance until its first large customer asks for it. Design a stable application identity, select the methods users need and make recovery, authorization and offboarding part of the original scope.
If you are planning or modernizing a mobile application, Actiknow can discuss the application architecture, integration requirements and identity lifecycle with your team. Share your user groups, target platforms and enterprise constraints through the Actiknow contact page to start a focused conversation.