
A practical guide to protecting critical workflows from third-party API changes
An API can return 200 OK while a business workflow breaks
Consider a customer-to-billing integration that receives a successful API response but no longer recognizes the customer’s status. The nightly synchronization completes. Its technical dashboard stays green. Yet the wrong customers are treated as eligible, invoices are held or downstream reports become unreliable. A change can be operationally serious without producing an HTTP error.
That is the central reason for API contract testing. Instead of asking only whether a vendor endpoint responds, teams verify whether its requests, responses and behavior still satisfy the assumptions on which their applications depend. For CTOs and operations leaders, the objective is early detection, accountable ownership and controlled recovery, not a promise that external systems will never change.
What is API contract testing?
An API contract describes the observable interface between a provider and a consumer. It may cover endpoint paths, methods, request parameters, required response fields, types, nullability, accepted values, error formats, pagination, authentication and event structures. It can be expressed as an OpenAPI document, JSON Schema, consumer-driven expectations, approved examples or a combination.
A contract test checks compatibility at that boundary. It is narrower than a complete end-to-end workflow test and more meaningful than a basic connectivity probe. A request that returns 200 with an empty identifier may be structurally valid HTTP but unusable for a customer reconciliation process.
The OpenAPI Specification provides a standardized description of HTTP APIs, including operations, parameters, responses and schemas. A specification is a useful source of truth when maintained, but it cannot by itself prove that a live vendor implementation matches the documentation or that a field’s business meaning has remained stable.
Why conventional integration testing often misses vendor changes
Old mocks test old assumptions
A mock response copied from a vendor six months ago is useful for local development. Unless it is periodically compared with approved vendor behavior, it only proves that the consumer still handles a six-month-old response. Every important fixture needs a version, an owner and a refresh policy.
Happy-path tests ignore dangerous edge cases
A test that retrieves one customer may miss a newly nullable identifier, an unexpected status, a second page of results, a changed error shape or a token with insufficient scopes. These edge cases can cause missing records, duplicate transactions and incorrect access decisions.
Schema validity is not business correctness
A field may remain numeric while its unit changes from dollars to cents. A status can remain a string while its meaning changes from an internal code to a display label. These changes require business invariants and reconciliation tests, not merely a JSON validator.
Begin with a risk-ranked inventory
Do not start by testing every endpoint equally. First identify integrations whose failure could interrupt billing, order fulfillment, customer entitlements, payroll, regulatory reporting or executive decision-making. Rank them by business consequence, data sensitivity, vendor change frequency and recoverability.
For each critical dependency, record the vendor and product, API version, endpoint and method, authentication scope, required fields, downstream consumers, pagination and retry rules, technical owner, business owner, vendor change-notice channel, test environment and replay or reconciliation method. The inventory should reveal which field changes would materially alter a business process.
For example, customer.external_id may be the join key that prevents duplicate billing accounts. That field deserves a hard validation gate. An optional description used only in an admin screen may need a lighter check. Actiknow’s custom solutions services include API-based system integrations and automation, where interface controls belong in the architecture from the beginning.
Classify changes by consumer impact, not by how they look
Compatible
An added optional response field is generally compatible when the consumer ignores unknown properties. A new endpoint is usually harmless to an existing client. But a strict parser may reject extra fields, so compatibility must be tested against the actual consuming code.
Review required
New enum values, changed default sorting, altered date precision, additional response variants, changes to optional nullability and modified rate-limit behavior deserve explicit review. A new status such as ON_HOLD may be syntactically valid but have no safe billing interpretation.
Breaking
Removing a consumed field, changing an identifier’s type, making a previously optional request parameter mandatory, narrowing accepted input, removing an endpoint or changing the meaning of a required field can break existing consumers. These changes need a migration plan, vendor coordination or an intentional release block.
Security-sensitive
New personal-data fields, unexpected confidential attributes, changed OAuth scopes and webhook signature changes require security review even when the API still functions. Keep security classification separate from ordinary schema compatibility.
The same logic applies beyond application integrations. Actiknow’s guide to handling schema drift discusses compatibility classes, quarantine and controlled downstream changes in data pipelines.
Build three layers of contract protection
Layer 1: specification and schema comparisons
Where the vendor publishes an OpenAPI document, store a versioned copy and compare it with the approved baseline. Detect removed operations, new required parameters, changed types, removed fields, nullability changes and enum differences. Retain a machine-readable diff as a build artifact. If no reliable specification exists, document a smaller consumer-owned contract covering only the fields and behavior your workflow needs.
Prefer targeted validation over exact snapshots of entire responses. Require stable identifiers and essential fields, allow safe additions and explicitly flag changes that would compromise processing. Use synthetic or sanitized fixtures. Do not commit production credentials or unnecessary personal data to a testing repository.
Layer 2: executable consumer expectations
Test the transformation and business mapping logic against approved and adverse examples. Verify missing identifiers, null values, unknown status codes, time zones, changed numeric precision and invalid date formats. For write operations, test duplicate prevention and idempotency after retries.
Consumer-driven tools such as Pact are useful when the provider can verify the consumer’s expectations. Pact Broker compatibility checks can establish whether specific tested consumer and provider versions are safe to deploy together. With an independent SaaS vendor that does not run your tests, do not assume provider-side verification exists. Your organization still needs its own checks.
Layer 3: safe checks against the vendor
Run scheduled read-only probes against the vendor sandbox or a permitted test tenant. Validate representative payloads, pagination and documented error behavior. If the sandbox differs from production, consider a narrowly scoped non-mutating production canary only when vendor terms, permissions and rate limits allow it. Do not create real charges or modify customer records merely to test a contract.
Record the environment, API version, credential scope, response fingerprint and first observed failure time. A passing sandbox test does not prove every production tenant or region behaves identically.
A concrete example: customer status synchronization
Assume a CRM sends eligible customers to a billing platform. The consumer requires a nonempty string id, a status and a parseable updated_at timestamp. It should accept a new optional display_name field without breaking. A simplified JSON Schema-style response check is:
{
“type”: “object”,
“required”: [“id”, “status”, “updated_at”],
“properties”: {
“id”: {“type”: “string”, “minLength”: 1},
“status”: {“type”: “string”, “minLength”: 1},
“updated_at”: {“type”: “string”, “format”: “date-time”}
}
}
This checks shape, not the meaning of status. Add a separate mapping rule: ACTIVE maps to eligible; SUSPENDED maps to hold; any unrecognized value enters a reviewable exception queue. A negative test containing status ON_HOLD should prove that the system does not silently treat it as ACTIVE. Depending on the JSON Schema validator, date-time format validation may need to be enabled explicitly.
This is an illustrative contract, not a claim about a particular vendor’s API. In a real integration, define required fields and permitted values from the actual documented behavior and the consumer’s business requirements.
The essential test matrix
Structure and request behavior
Test removed required fields, changed types, null identifiers, nested objects becoming arrays, unknown enum values, new mandatory request parameters, content-type changes, invalid requests and altered validation errors. Include empty collections and unexpected but syntactically valid responses.
Pagination, extraction and state
Test the first, middle and final page; empty pages; cursor continuation; rate-limited pages; duplicate IDs; records changing during extraction; and recovery after a failed page. For incremental feeds, verify inclusive versus exclusive timestamp boundaries, timezone precision and identical update timestamps.
Authentication, webhooks and retries
Test expired tokens, insufficient scopes, revoked access, signature verification, duplicate webhook delivery, out-of-order events, unknown event types and replay. A timeout after POST may mean the provider completed the action before the response was lost. Never blindly retry non-idempotent writes without an idempotency key or equivalent duplicate protection.
Contract checks work best alongside reliable transport behavior. Actiknow’s guide to API rate limits, retries and webhooks explains throttling, idempotency, replay and monitoring controls that complement interface validation.
Where contract tests belong in the delivery process
Pull requests and continuous integration
Run fixture-based schema and mapping tests whenever integration code changes. Compare a newly published vendor specification with the approved version. Fail the affected build on an unapproved breaking change and provide a readable field-level diff. Do not block unrelated services for harmless additive changes.
Scheduled vendor checks
Run external probes independently of internal releases. Select cadence according to business criticality, vendor volatility and quota. A nightly check may be enough for some feeds; a critical real-time workflow may require more frequent permitted checks. Alerts should identify the endpoint, contract version, environment, affected business workflow and accountable owner.
Vendor version migrations
Run the same consumer fixtures against old and new API versions. Verify authentication scopes, error responses, pagination and business mappings. Where practical, use parallel reads or shadow validation before cutover. Keep a rollback plan and record the last compatible version.
After production deployment
Monitor source-to-target completeness and business outcomes. A technically compatible API can still lose records through filtering, permissions, race conditions or unexpected volume. Reconcile identifiers, counts and critical states, and preserve a controlled replay path.
A useful failure response playbook
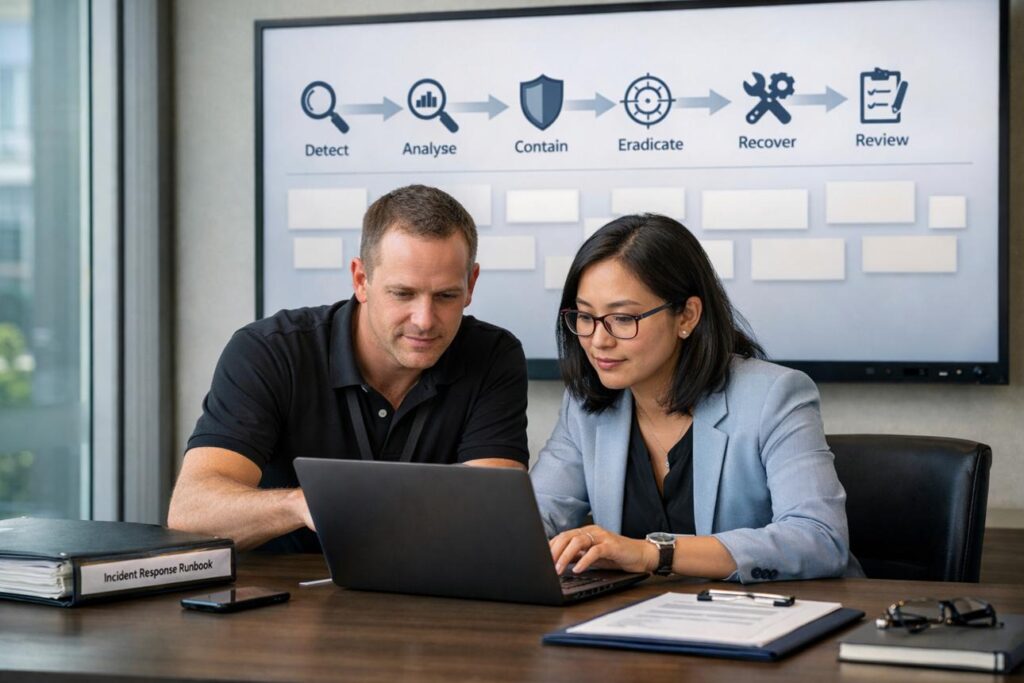
First establish whether the alert reflects genuine vendor drift, an expired test credential, an outage, a changed sandbox or an obsolete fixture. Capture a sanitized response diff, timestamp, environment, version and downstream impact. Never include secrets or sensitive payloads in the alert.
Then classify severity. A new unused field may need only a reviewed fixture update. A missing invoice identifier should quarantine affected records or stop that specific workflow. A security-sensitive change should be escalated to the security owner. Contain the impact without unnecessarily disabling unrelated integrations.
Finally choose a recovery action: update the mapping, pin a supported version, request vendor clarification, use a documented fallback, replay failed records or pause writes. After recovery, reconcile the exposure window. A green test after a fix does not prove that previously missed records were recovered.
Ownership and governance
The integration engineer owns executable tests, fixtures and CI gates. A platform or security owner manages credentials, environments and sensitive-data handling. The business owner defines acceptable outcomes and signs off on high-risk mapping changes. A vendor relationship owner monitors release notices, deprecation schedules and escalation channels.
Every critical integration should have a named primary technical owner, backup, business decision-maker and runbook. A shared inbox is not a substitute for accountability. Record approved exceptions with an expiry date and a reason, then revisit them before the vendor migration deadline.
A 30-day implementation plan
Week 1: map the exposure
Choose five to ten critical operations. Inventory consumed fields, business dependencies, API versions and owners. Collect vendor specifications and sanitized examples. Identify blind spots such as no unknown-enum handling or no replay capability.
Week 2: create the executable baseline
Store contracts and fixtures in version control. Implement positive and negative tests for missing required fields, nulls, unknown statuses, type changes and duplicate writes. Add mapping assertions so syntactically valid but unsupported values are handled safely.
Week 3: automate detection
Add build-time tests and scheduled vendor probes where feasible. Route failures to named owners with a readable diff. Define severity, escalation and approval rules. Subscribe to vendor change notices, but do not rely on them as the sole detection mechanism.
Week 4: rehearse and validate recovery
Simulate a removed identifier or new status in a controlled environment. Confirm the test catches it, the workflow contains it, the owner receives the alert and the affected records can be replayed or reconciled. Review the exercise with the business owner before expanding coverage.
What executives should measure
Critical-operation coverage measures the share of high-impact API operations with executable consumer checks. Change detection time measures how long observable drift remains unnoticed. Escaped contract defects count incompatibilities that reached production workflows. Mean restoration time measures the time from confirmed incompatibility to resumed safe processing.
Also track stale fixtures, unresolved breaking changes, vendor notice lead time, exception queue age and source-to-target reconciliation gaps. Report them by business workflow. A headline test-coverage percentage is misleading if low-value endpoints are well tested but billing or entitlement flows are not.
Avoid promising a universal detection SLA. Choose targets based on risk, vendor constraints and an observed baseline. Contract testing reduces exposure; it cannot guarantee that a third party will never make an incompatible change.
Common mistakes
Avoid exact-response snapshots that reject every harmless optional field. Avoid ignoring new enum values when they control payments or access. Do not assume sandbox behavior is identical to production. Do not equate 200 OK with business success. Do not keep stale mocks indefinitely. Do not put production secrets or personal data in test fixtures. Do not treat vendor release notes as a replacement for testing.
Above all, do not confuse structural compatibility with data completeness. Pagination errors, missing events, changed filters and semantic drift can occur even when the response schema is unchanged. Pair contract tests with operational monitoring and reconciliation.
Frequently asked questions
1. How is contract testing different from integration testing?
Contract tests verify interface expectations at the provider-consumer boundary. Integration tests verify that components work together across a broader workflow. Both are valuable; contract tests are usually faster to run and diagnose.
2. Do we need access to the vendor’s source code?
No. You can test your own consumer against documented contracts and approved examples, then run permitted probes against the vendor. Provider-side consumer-driven verification requires cooperation or control of the provider.
3. Is an OpenAPI specification enough?
No. Documentation can lag the implementation, and structural schemas do not capture every business rule. Combine specification comparison with executable consumer checks and live validation.
4. Is adding a response field a breaking change?
Often not, if the consumer ignores unknown fields. It can break strict decoders or create security concerns. Test the actual consumer rather than assuming compatibility.
5. Why do new enum values matter?
A new status may be valid JSON but unsupported by downstream decisions. Explicitly test unknown values and route them to a safe exception path.
6. Should every failed test block deployment?
No. Apply risk-based gates to the affected workflow. An unused optional field may need review, while a missing payment identifier or changed authentication requirement demands stronger action.
7. How often should vendor probes run?
Use business criticality, vendor change frequency, rate limits and test environment quality to set the cadence. Scheduled probes supplement CI tests and production monitoring.
8. Can tests catch a change from dollars to cents?
Only if you encode business invariants or reconciliation rules. A number-type check alone cannot detect a unit change.
9. What should we test for webhooks?
Validate signatures, required fields, duplicate events, ordering assumptions, replay, unknown event types and idempotent downstream processing.
10. What is the smallest worthwhile pilot?
Select one high-impact integration, document its critical assumptions, create negative fixtures, automate them in CI and assign an owner for live checks. Prove detection and recovery before scaling.
Conclusion: make vendor changes manageable
Vendors will change their APIs, and applications must evolve with them. The goal is not to freeze an interface. It is to detect incompatibility before it causes a silent business error, contain the affected workflow and give accountable teams a tested recovery path.
For organizations assessing fragile integrations or designing new multi-system workflows, Actiknow can help review API dependencies, field mappings and the validation and recovery controls to include in the solution. Discuss your integration requirements with Actiknow.
Technical references
The OpenAPI Specification defines a machine-readable HTTP API description. Pact’s can-i-deploy documentation explains version-based compatibility checks when provider verification results are available.