Growth creates a data problem long before most companies call it a governance problem.
A sales team changes the definition of an active customer. Finance closes the month using a spreadsheet that does not quite match the CRM. Marketing has its own channel taxonomy. Operations exports data into shared files. A new dashboard exposes discrepancies that had been hidden for years. Meanwhile, more employees, vendors, applications, and automated pipelines are gaining access to increasingly sensitive information.
The instinctive response is often to buy a governance platform or launch a large enterprise program. For a growing company, that is usually the wrong starting point. Data governance is not primarily a software purchase. It is a management system for deciding who is accountable for important data, what key terms mean, who can access information, how quality is monitored, and how changes are controlled.
The objective is not to govern every field in every system. It is to make the data that drives important decisions trustworthy, understandable, appropriately protected, and maintainable.
What data governance should accomplish
A useful governance program should answer six practical questions:
- Who owns this data and the business definition behind it?
- What exactly does this metric or field mean?
- Who is allowed to see or change it?
- How do we know whether it is complete and accurate enough for its purpose?
- How long should we retain it, and when should we remove it?
- What happens when a source, definition, transformation, or report changes?
If your governance initiative cannot answer those questions for your most important datasets, adding more tooling will not solve the underlying problem.
For companies building dashboards across databases, APIs, spreadsheets, and operational platforms, Actiknow’s business intelligence services illustrate the type of environment in which these questions become important: multiple sources are integrated so that data can be analyzed and reported consistently.
Start with business-critical data, not the entire estate
A common governance mistake is attempting to catalog everything at once. A growing company may already have hundreds of tables, thousands of spreadsheet columns, SaaS applications, historical exports, and duplicate definitions. Treating every data element as equally important creates months of documentation with little visible business value.
Start with the information used to run the company.
That typically includes executive KPIs, financial reporting measures, sales pipeline and revenue data, customer and account identifiers, operational service metrics, employee or supplier information where relevant, and sensitive personal or commercial data.
A simple prioritization test is to ask: if this number were wrong tomorrow morning, would someone make a materially different decision, report the wrong result, breach an obligation, or waste significant time reconciling it?
If yes, it belongs near the front of the governance queue.
1. Establish ownership before writing policies
Every critical data domain needs a business owner. Ownership does not mean that the person maintains database tables. It means someone has authority to resolve questions about meaning, acceptable use, and business rules.
For example, Finance may own recognized revenue, Sales Operations may own pipeline stage definitions, Marketing may own campaign taxonomy, and HR may own employee classifications. Technology or data teams can implement these rules, but they should not quietly become the business owner simply because they build the pipeline.
For each critical metric or dataset, document a business owner and a technical custodian. The business owner decides what the information means. The technical custodian understands where it comes from, how it moves, and what can break.
This distinction prevents one of the most damaging patterns in analytics: engineers being forced to make business-policy decisions because nobody else has explicit accountability.
Growing organizations often have several technically correct versions of the same metric. Revenue may mean invoiced revenue, recognized revenue, booked revenue, cash collected, or annual contract value. An active customer may mean a paying customer, a customer with an open contract, or anyone who has used the product in the last 30 days.
The problem is not necessarily that one definition is wrong. The problem is that people use the same label for different concepts.
For each executive KPI, document:
- Business name and plain-English definition
- Calculation logic
- Included and excluded populations
- Date basis and timezone
- Source system or authoritative dataset
- Owner
- Refresh frequency
- Known limitations
Do not start with hundreds of definitions. Start with the 20 to 40 measures that repeatedly appear in executive, finance, sales, marketing, and operational reviews.
Where multiple definitions are legitimately required, name them explicitly. “Revenue” is ambiguous. “Recognized revenue,” “booked revenue,” and “cash collected” are much harder to confuse.
3. Put access governance around the data, not only the dashboard
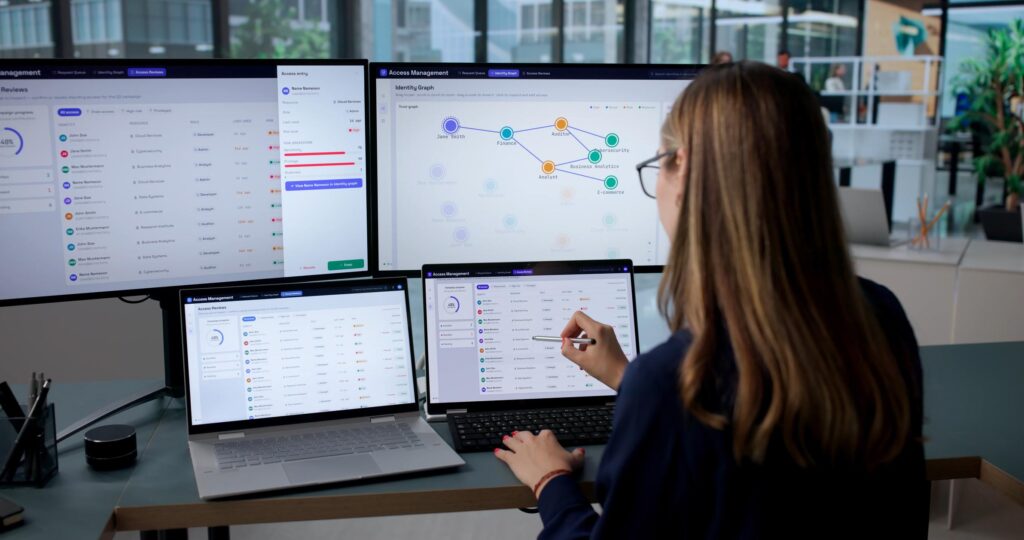
Dashboard permissions are only one layer of access control. The same information may also exist in the warehouse, CRM, exported CSV files, spreadsheets, API credentials, notebooks, staging environments, backups, and automated integrations.
Governance therefore needs to consider the full path of the data.
A practical access model starts with least privilege: users and services receive the minimum access required for their role. Sensitive fields should be classified, and access should be reviewed when employees change roles or leave the organization. Service accounts and integration credentials deserve the same scrutiny as human users.
Actiknow’s published data security practices describe controls such as encrypted connections, minimum necessary permissions, OAuth where possible, multifactor authentication, and least-privilege IAM. These are useful examples of the technical controls that should support, rather than replace, governance decisions.
Access reviews should also distinguish between the ability to view data and the ability to change source records, transformations, definitions, or reports. Those are very different risks.
4. Define data quality in business terms
“Clean data” is not a measurable standard. Data quality should be tied to how the information is used.
A customer email field used for a marketing campaign may need a high validity rate. A daily executive revenue dashboard may need completeness through the prior business day. A regulatory or financial report may require stricter reconciliation and traceability than an exploratory marketing analysis.
Useful quality dimensions include completeness, validity, uniqueness, consistency, timeliness, and reconciliation to an authoritative source.
For critical datasets, define a small number of tests that indicate whether the data is fit for purpose. Examples include duplicate customer IDs, missing transaction dates, unexpected nulls in required fields, sudden row-count changes, pipeline freshness, totals that no longer reconcile to the source system, or values outside accepted ranges.
The important step is deciding what happens when a test fails. A quality check that nobody owns is only an automated warning.
5. Create retention rules before storage becomes permanent by accident
Cloud storage is inexpensive enough that companies can keep data indefinitely without consciously deciding to do so. That convenience can create operational, security, privacy, and legal complexity.
Retention should be intentional.
For major data categories, determine why the information is retained, how long it is operationally or legally useful, whether historical aggregates can replace detailed records, and how deletion should propagate to downstream systems where required.
Do not let the warehouse become an unofficial archive for every historical extract simply because nobody has decided what can be removed.
Retention rules should be developed with the appropriate legal, privacy, finance, and security stakeholders. Governance provides the operating mechanism, but it should not invent legal retention periods.
6. Introduce change control for metrics and pipelines
Many reporting failures are not caused by bad data. They are caused by valid changes that were not communicated downstream.
A CRM administrator renames a stage. An application team changes an enum. Finance updates a revenue rule. An API version changes. A field is deprecated. A transformation is modified to fix one dashboard and silently changes three others.
Critical data changes need a lightweight change-control process.
At minimum, record what is changing, why it is changing, which datasets and reports depend on it, who approved the business-definition change, how the change will be tested, and when it will reach production.
For high-impact reporting, parallel validation is valuable. Run the old and new logic together for an agreed period, investigate differences, and obtain business sign-off before retiring the old version.
7. Build traceability without trying to document the universe
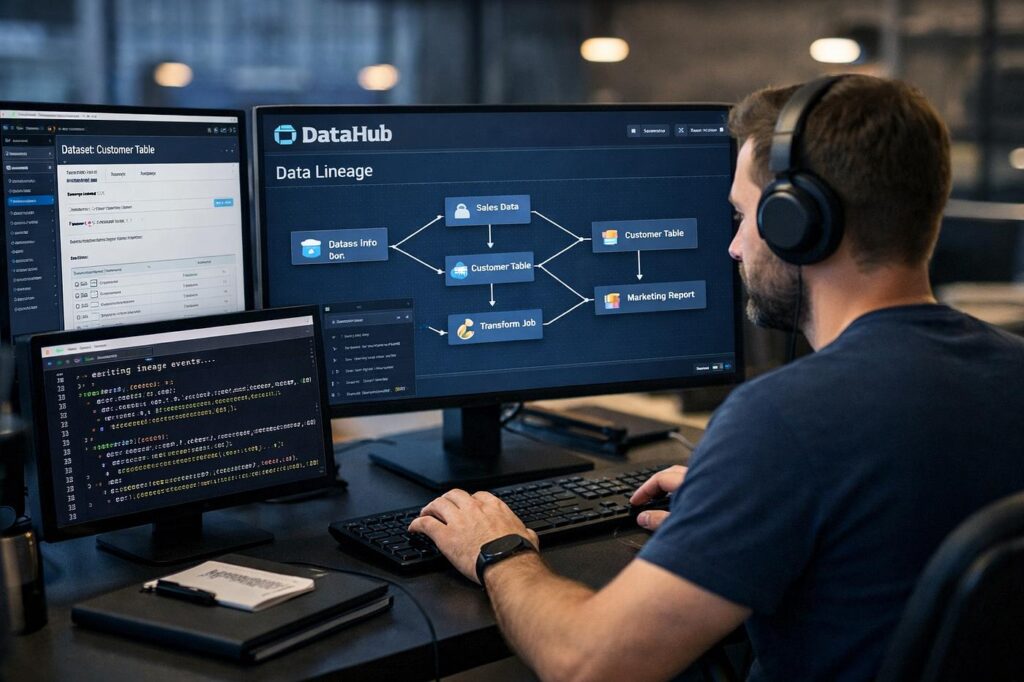
When an executive asks why a number changed, the data team should be able to trace it back through the reporting model, transformation logic, and source system.
This is lineage in practical terms.
You do not need perfect automated lineage on day one. Start by documenting the path for the handful of metrics that matter most. Identify the source, transformation, business rule, output dataset, and reports that consume it.
This becomes especially important as a company expands its analytics environment. Actiknow’s BI consulting offering includes integrating data from diverse databases and APIs, an architecture pattern in which source-to-report traceability becomes increasingly valuable as the number of systems grows.
8. Separate governance from bureaucracy
A governance program fails when employees experience it only as forms, approvals, and delays.
The best governance mechanisms make correct behavior easier. A certified dataset is easier to find than an unofficial export. A clear metric dictionary prevents meetings about definitions. Role-based access avoids repeated manual permission decisions. Automated quality tests identify problems before executives see them. Version-controlled transformations make changes easier to review and reverse.
Governance should reduce organizational friction, not add ceremonial process.
A practical 90-day starting plan
During the first 30 days, identify the 10 to 20 datasets and 20 to 40 metrics that matter most. Assign business owners and technical custodians. Map the systems in which sensitive or business-critical information resides. Document the most obvious definition conflicts.
During days 31 to 60, publish the first metric dictionary, classify sensitive fields, review access to critical data, establish basic quality tests, and document source-to-report lineage for the most important executive measures.
During days 61 to 90, introduce lightweight change control, define escalation for failed quality tests, establish an access-review cadence, begin retention discussions with the appropriate stakeholders, and measure whether reconciliation effort and recurring reporting disputes are declining.
This is enough to create a functioning governance foundation without turning governance into a year-long transformation program.
What should you measure?
Governance itself should have operational metrics. Useful measures include the percentage of critical KPIs with named owners, percentage with approved definitions, percentage of critical datasets covered by quality checks, unresolved data-quality incidents, time to resolve reconciliation issues, stale user or service-account access, and changes to critical logic that passed documented review.
Avoid vanity measures such as the total number of cataloged fields unless catalog coverage is directly helping users find and trust data.
When do you need dedicated governance software?
Spreadsheets, documentation tools, warehouse metadata, identity systems, and existing ticketing workflows can support an early governance program. Dedicated catalog, lineage, quality, or governance platforms become more valuable as the number of systems, users, regulated datasets, domains, and dependencies grows.
The trigger should be operational complexity, not a desire to appear mature.
Before buying a platform, make sure the organization has already decided who owns critical data and how definitions, access, quality, and changes will be managed. Software can automate a governance operating model. It cannot create accountability where none exists.
Frequently Asked Questions
What is data governance in simple terms?
Data governance is the set of responsibilities, definitions, controls, and processes used to ensure important organizational data is understood, trustworthy, appropriately accessible, and managed throughout its lifecycle.
Does a small or mid-sized company need data governance?
It needs governance wherever data materially affects decisions, financial reporting, customer operations, security, privacy, or compliance. The program does not need to resemble a large-enterprise governance office. A lightweight model focused on critical data is often more useful.
Who should own data governance?
Business leaders should own the meaning and acceptable use of data in their domains, while technology and data teams typically act as technical custodians. A cross-functional leader or governance group can coordinate standards and resolve issues that span domains.
What should we govern first?
Start with executive KPIs, financial measures, customer and revenue data, sensitive information, and datasets that repeatedly create reconciliation problems. Prioritize based on decision impact and risk.
Is a data catalog the same as data governance?
No. A catalog can help document datasets, definitions, metadata, and lineage. Governance is broader. It includes ownership, decision rights, access, quality, retention, and change management.
How do we know whether governance is working?
Look for fewer recurring metric disputes, faster reconciliation, clearer ownership, fewer inappropriate access paths, earlier detection of quality failures, and more controlled changes to critical reporting logic.
Should every metric have one universal definition?
Not necessarily. Different business purposes can require different valid measures. Governance should make those differences explicit, give them distinct names, document their calculation, and prevent ambiguous labels from being treated as interchangeable.
A sensible next step
If your organization is already spending too much time reconciling dashboards, debating definitions, or managing reporting across disconnected sources, begin with the critical decisions and data domains rather than a large governance tool purchase.
Actiknow works on business intelligence implementations, dashboards, integrations, data analysis, and reporting automation. If you are evaluating how to structure a more reliable analytics environment, you can discuss your BI and data requirements with Actiknow.